Build more secure applications with structured application security testing, secure code review and vulnerability-focused guidance across the software development lifecycle. Cylentrix works at the source-code and application layer, helping engineering teams strengthen secure coding practices, software security and DevSecOps workflows across web, API and mobile applications.
Security Controls Across the Application Lifecycle
Application security is the practice of finding and reducing security risk in software: how it is designed, how the source code is written, how it authenticates users and how it is deployed. These eight services can be engaged individually or as one programme.
Secure Code Review
Review source code to identify security weaknesses, insecure coding patterns and potential vulnerabilities.
Application Security Testing
Assess applications for security weaknesses through testing approaches suited to the technology and scope.
Web Application Security
Evaluate web applications for common security risks and application-layer vulnerabilities.
API Security Assessment
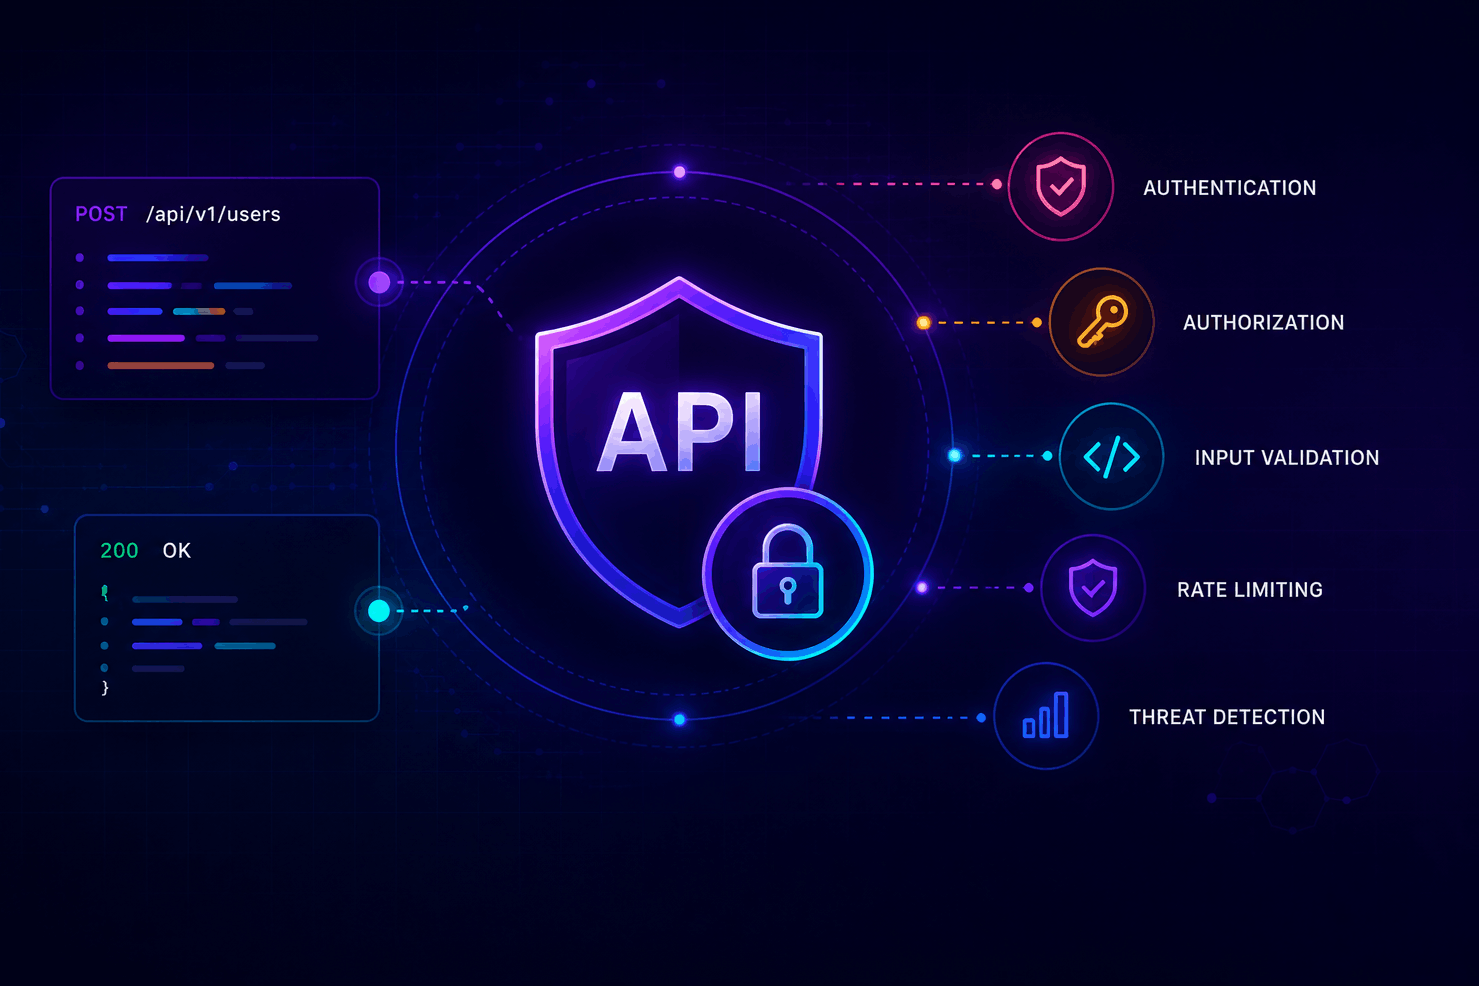
Assess APIs for authentication, authorisation, input validation and other relevant security risks.
Mobile Application Security
Review mobile applications and their supporting components for security weaknesses.
Authentication & Authorization Review
Evaluate application access controls, session handling and authorisation logic.
Dependency & Component Risk
Identify security concerns in third-party libraries, packages and software supply chain components.
Security Configuration Review
Assess application and platform security configurations that materially affect application risk.
02APPROACH & PROCESS
From Source Code to a Verified Fix
Secure code review examines the logic behind the application, not only its outward behaviour. That is where flawed authorisation checks, unsafe defaults and hardcoded secrets live, and where they can still be fixed cheaply.
Source Code
Scope repositories, languages, frameworks and critical modules.
Security Analysis
Manual review and static analysis across security-relevant code paths.
Findings
Weaknesses documented with affected code, context and evidence.
Risk Prioritization
Severity, exploitability and business impact applied to each finding.
Developer Guidance
Practical fix direction written for the team that owns the code.
Remediation
Engineering teams apply changes with security support where needed.
Validation
Fixes retested to confirm the weakness is genuinely closed.
Code review can be performed manually, with automated tooling, or through a combination of both depending on the application and engagement requirements
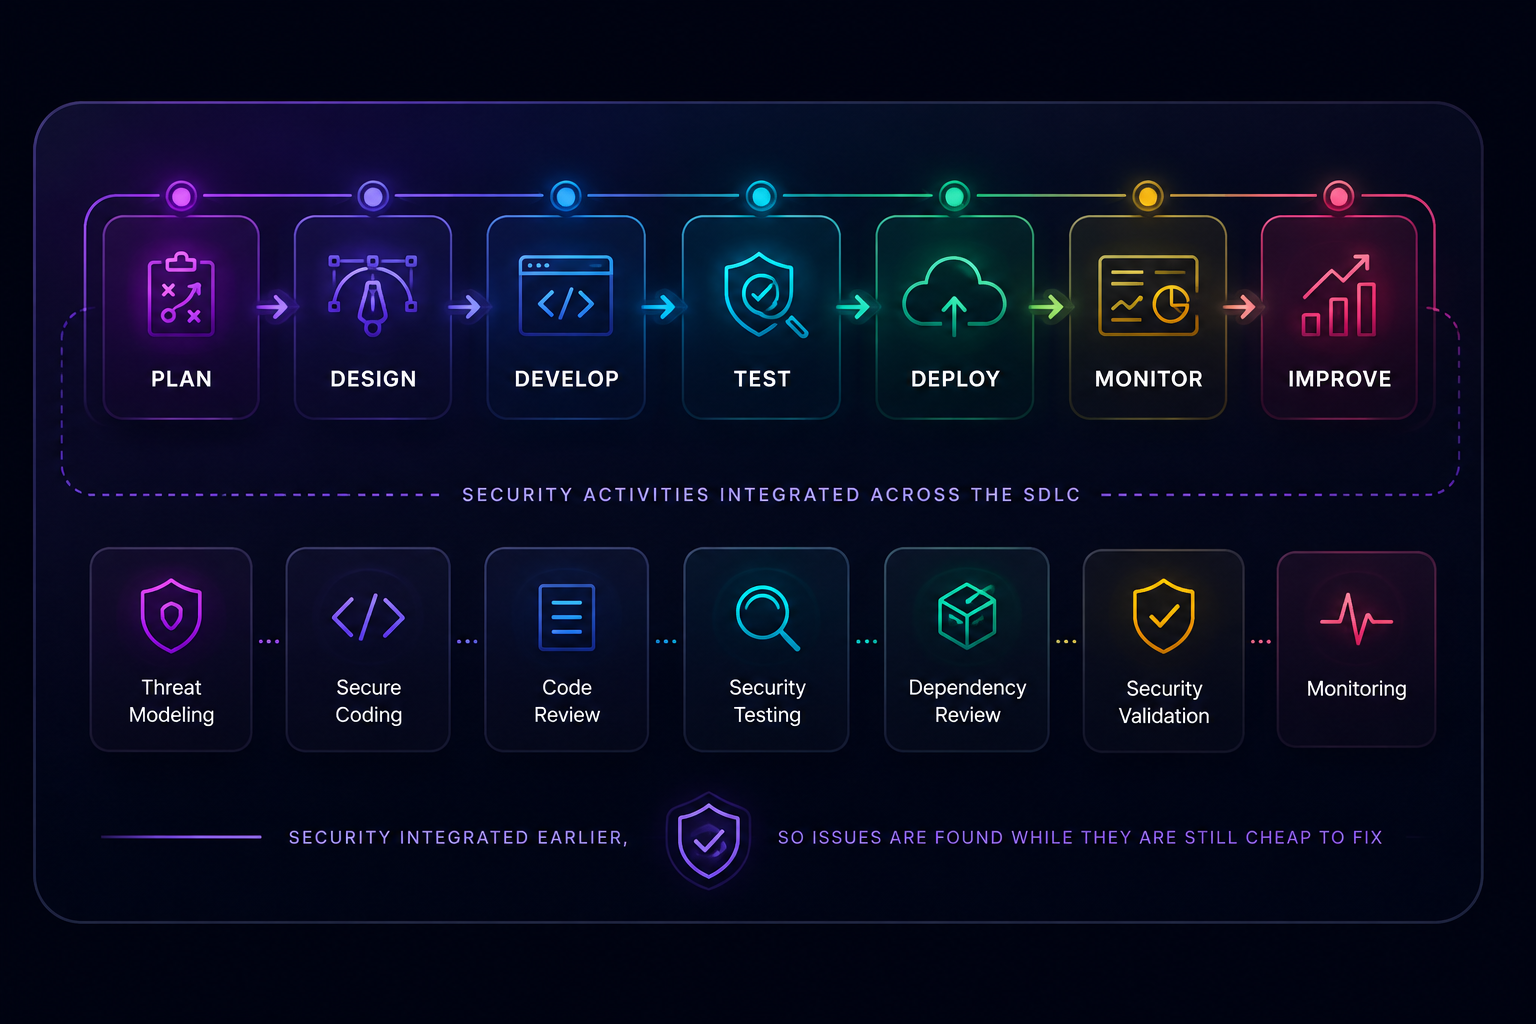
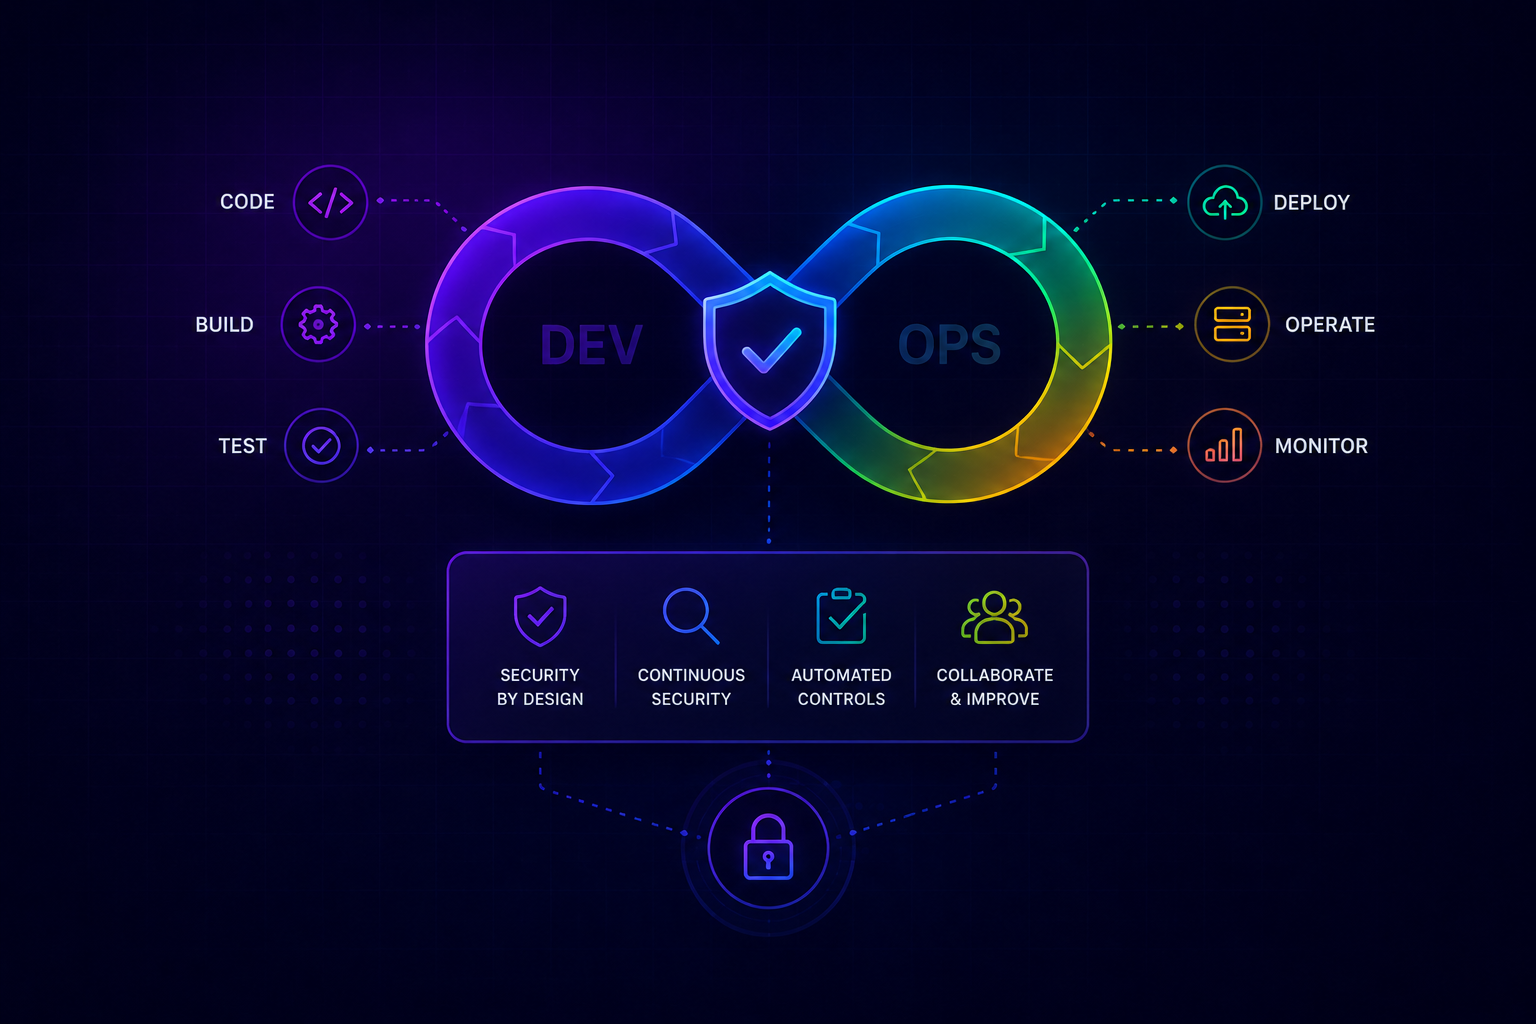
The same work runs inside your delivery pipeline rather than beside it. DevSecOps integration places threat modelling, secure coding, code review, security testing and dependency review at the points in the software development lifecycle where each is cheapest to act on. It does not, on its own, guarantee vulnerability-free software: automated checks still need tuning, human validation and engineering judgment.
03BUSINESS BENEFITS
Turn Security Findings Into Action
Identifying vulnerabilities is only one part of application security. The value shows up when findings are validated, ranked honestly and closed with a fix the development team can actually ship.
Risk Prioritization
Findings ranked against real conditions rather than a raw scanner score, so effort goes to what matters first.
Developer Guidance
Each finding explained with affected code, why it matters and a fix direction the engineering team can act on.
Remediation Tracking
Open findings tracked to closure with clear ownership, status and agreed timelines across releases.
Validation & Retesting
Retesting after remediation confirms the weakness is closed and that the fix has not introduced a new one.
Findings are prioritized against
Severity
Exploitability
Business impact
Affected assets
Exposure
Application context
04INDUSTRIES
Industries that run on business-critical software
Wherever an application holds customer data, moves money or carries a regulated process, the source code behind it is part of the security perimeter. These are the sectors where Cylentrix application security work concentrates.
Manufacturing
MES interfaces, supplier portals and IIoT APIs connect the plant floor to partners and cloud services.
Healthcare
Patient portals, health apps and record-system integrations handle sensitive data under strict rules.
BFSI
Banking journeys, payment APIs and onboarding flows where authorisation logic has to be exact.
IT & Technology
Product teams shipping SaaS platforms and APIs need review that keeps pace with the release cycle.
Education
Learning platforms, admission systems and student portals hold records for large user populations.
Retail
Storefronts, checkout flows and payment integrations sit directly on the customer path.
Logistics
Tracking portals, warehouse apps and partner APIs exchange data across many external parties.
Government
Citizen service portals and public-facing APIs carry identity workflows that must hold up to public scrutiny.
Data Centres
Management consoles and provisioning APIs control infrastructure through software.
Hospitality
Booking engines, guest apps and channel integrations process payment and traveller data continuously.
05WHY CYLENTRIX
Why enterprises choose Cylentrix for Application Security
Application security only works when the people reviewing the code understand both software engineering and the enterprise environment the software runs in. That combination is what Cylentrix brings to the engagement.
Security, IT and telecom in one team
Application findings are read in the context of the wider estate: identity, network, cloud and the systems the application depends on.
Secure code review expertise
Source-level review across authentication, authorisation, input handling, cryptographic usage and secrets management.
Security testing capability
Structured application security testing across web, API and mobile components, scoped to how the software is actually built.
Application and API depth
APIs are treated as first-class attack surface, with authorisation and data exposure tested across user boundaries.
Secure development practices
Guidance on threat modelling, secure coding standards and review gates that fit an existing delivery process.
Risk-based remediation guidance
Findings ranked by severity, exploitability and business impact so engineering effort goes where it reduces the most risk.
Developer-friendly reporting
Reports written for the people who will fix the code: affected files, why it matters and what a safe implementation looks like.
Enterprise security perspective
Application risk framed for regulated environments, audit expectations and executive reporting, not just a technical bug list.
India, USA and Singapore
Distributed engineering teams supported across three regions, under one security standard and one point of accountability.
06TECHNOLOGY & SECURITY PARTNERS
Technology & Security Partners
Application security tooling is selected to fit the languages, frameworks and pipelines already in use, so security review strengthens the existing engineering workflow instead of replacing it.
CheckmarxApplication security testing platform
FortifyStatic and dynamic code analysis
VeracodeApplication security testing and analysis
SnykDeveloper and dependency security
07WHITEPAPERS & RESOURCES
Practical guidance for engineering teams
Reference material from the Cylentrix application security practice, written for the developers, architects and security leads who own the software.
The questions engineering and security leaders ask before starting an application security or secure code review engagement.
What is Application Security?
Application security is the practice of identifying, reducing and managing security risk in software. It covers how an application is designed, how its source code is written, how it authenticates and authorises users, how it handles input and sensitive data, which third-party components it depends on, and how it is configured and deployed. It runs across the whole software development lifecycle rather than being a single test before release.
What is Secure Code Review?
Secure code review is a structured security review of application source code. Reviewers examine authentication and authorisation logic, input handling, sensitive data handling, error handling, cryptographic usage, secrets management and framework configuration to find insecure coding patterns and potential vulnerabilities. It can be performed manually, with automated static analysis tooling, or as a combination of both depending on the application, the languages involved and the scope of the engagement.
Why is code review important for application security?
Code review looks at the logic behind an application rather than only its external behaviour, so it can surface issues that black-box testing may not reach: flawed authorisation checks, unsafe defaults, weak cryptographic usage or hardcoded secrets. Reviewing code during development also puts findings in front of developers while the relevant code is still familiar, which usually makes remediation simpler than fixing the same issue after release.
What types of vulnerabilities can application security assessments identify?
An application vulnerability assessment commonly identifies weaknesses in authentication and session management, broken or missing authorisation checks, improper input validation and output handling, insecure API design, sensitive data exposure, weak cryptographic practices, exposed secrets, vulnerable third-party dependencies and insecure configuration. No assessment can guarantee that every possible vulnerability has been found, which is why testing is treated as a repeatable activity rather than a one-time exercise.
Can Cylentrix review web applications and APIs?
Yes. Cylentrix reviews web applications, APIs and mobile application components, along with the authentication, authorisation and data-handling logic that connects them. Because most modern applications expose a large part of their functionality through APIs, API security is treated as a core part of an application security engagement rather than an optional add-on.
When should security testing be performed during the SDLC?
Security work is most useful when it is spread across the lifecycle: threat modelling and security requirements during design, secure coding practices and code review during development, security testing before release, and validation and monitoring after deployment. Testing only at the end of a project tends to surface issues when they are most expensive and most disruptive to fix.
How does DevSecOps improve application security?
DevSecOps integrates activities such as dependency checks, static analysis, secrets detection and security testing into existing development and delivery pipelines, so issues appear as part of normal engineering workflow instead of a separate late-stage review. It improves consistency and shortens feedback loops, but it does not by itself guarantee vulnerability-free software: tooling still needs human validation, tuning and engineering judgment.
How can Cylentrix help with Application Security & Code Review?
Cylentrix supports enterprises with secure code review, application security testing across web, API and mobile components, dependency and configuration review, DevSecOps integration and risk-based remediation guidance written for developers. Findings are validated, prioritised by severity, exploitability and business impact, and retested after fixes, with engineering teams supported across India, the USA and Singapore.
GET STARTED
Build Security Into Every Line of Code
Identify application security weaknesses earlier, strengthen secure development practices and reduce software security risk with expert application security and code review. Tell us what you are building and we will scope the review around it.
Secure code review across your languages and frameworks
Web, API and mobile application security testing
Risk-based remediation guidance written for developers