Assess security controls, identify compliance gaps and strengthen governance with structured security audits and compliance readiness services aligned with ISO/IEC 27001, PCI DSS and GDPR. Cylentrix works alongside enterprise security and IT teams on control assessment, evidence readiness and prioritized remediation planning.
Turn security controls into audit-ready confidence
A security audit answers a question most organisations can only guess at: do our policies, processes and technical controls actually line up with our business needs and the requirements we are held to?
A security compliance audit is a structured review of what is in place, how it works day to day, and what evidence exists to demonstrate it. It looks across governance and documentation, operational process, and the technical controls protecting systems and data. The value is not the finding list. It is the clarity: a defensible view of current state, and a realistic path from there to where the organisation needs to be.
Cylentrix supports enterprises through that path with current-state assessment, control review, compliance gap assessment, evidence and documentation readiness, remediation planning and audit preparation. Assessments are scoped against the requirements that genuinely apply, whether that is ISO/IEC 27001, PCI DSS, GDPR security obligations, customer security questionnaires or an internal standard.
Our role is assessment and advisory. Certification, attestation and regulatory determinations rest with the relevant certification body, assessor or authority, and we are explicit about that boundary at every stage.
Control Assessment
Identify gaps across the security controls relevant to your scope, environment and requirements.
Compliance Readiness
Understand current readiness against the selected requirements before a formal audit or assessment.
Evidence Preparation
Organise the records and supporting documentation that show how controls operate in practice.
Remediation Planning
Prioritize improvements by risk and business context, so the plan can actually be delivered.
Frameworks we assess against
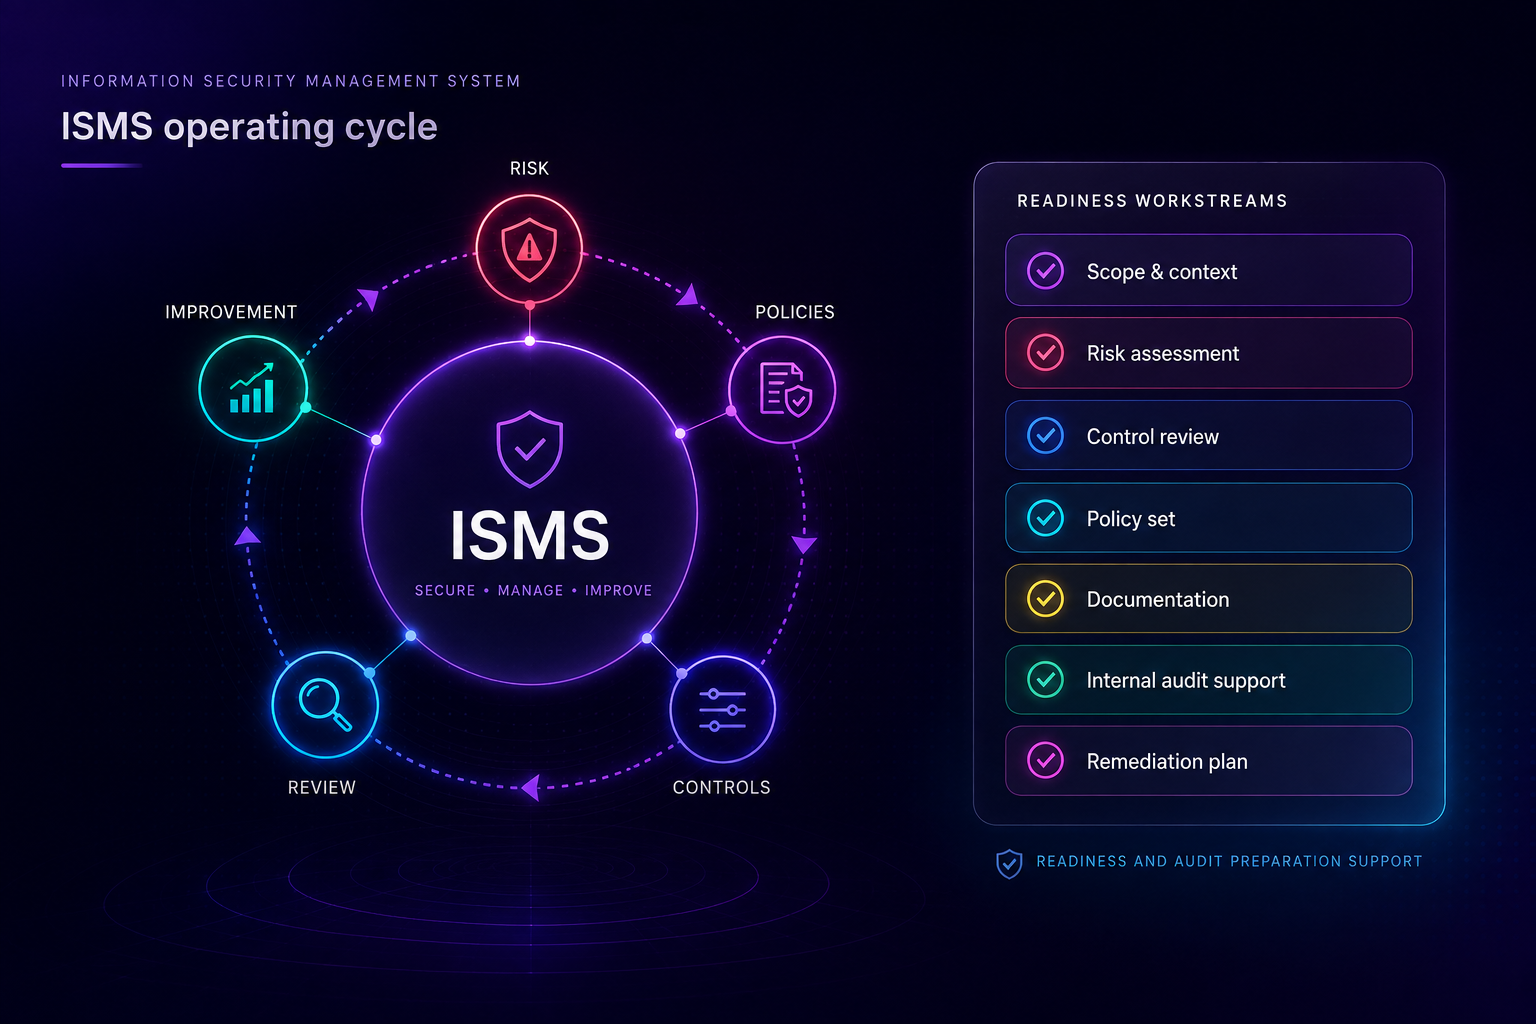
ISO/IEC 27001 Readiness
Review of the Information Security Management System: scope and context, information security risk assessment, policy and process documentation, control implementation and the records an auditor expects to see. Output is a gap list with owners and sequence.
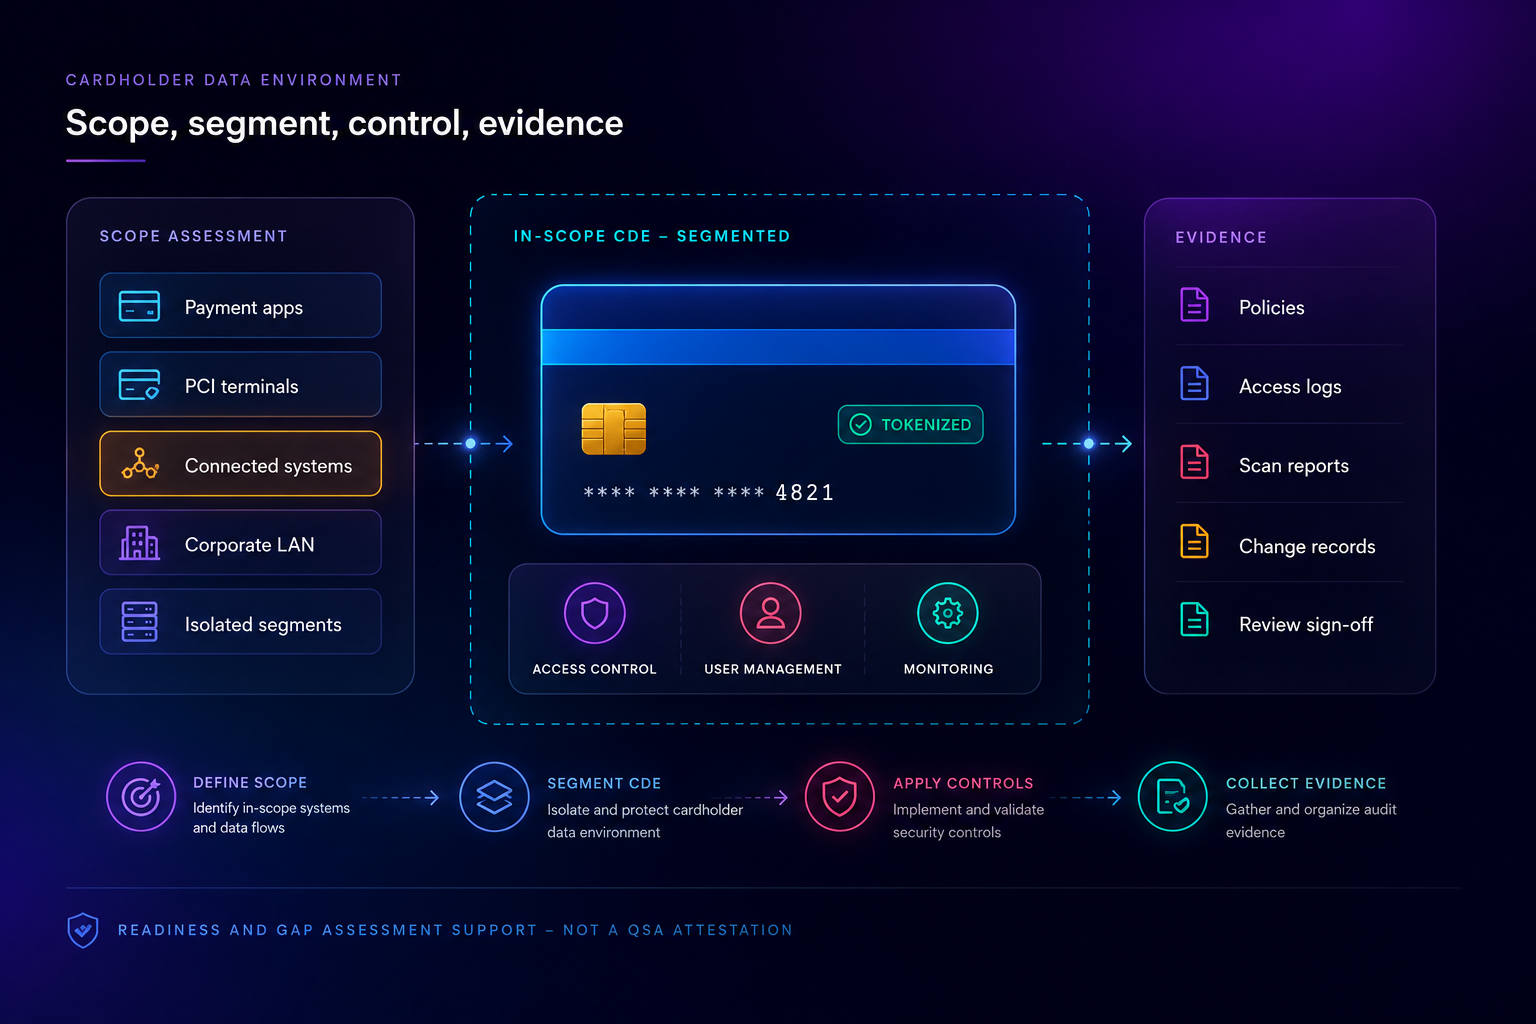
PCI DSS Compliance Readiness
Scope mapping of the cardholder data environment first: where card data enters, rests and moves, and what is genuinely segmented away. Then access management, vulnerability management and monitoring controls, with the evidence that supports them.
GDPR Security Readiness
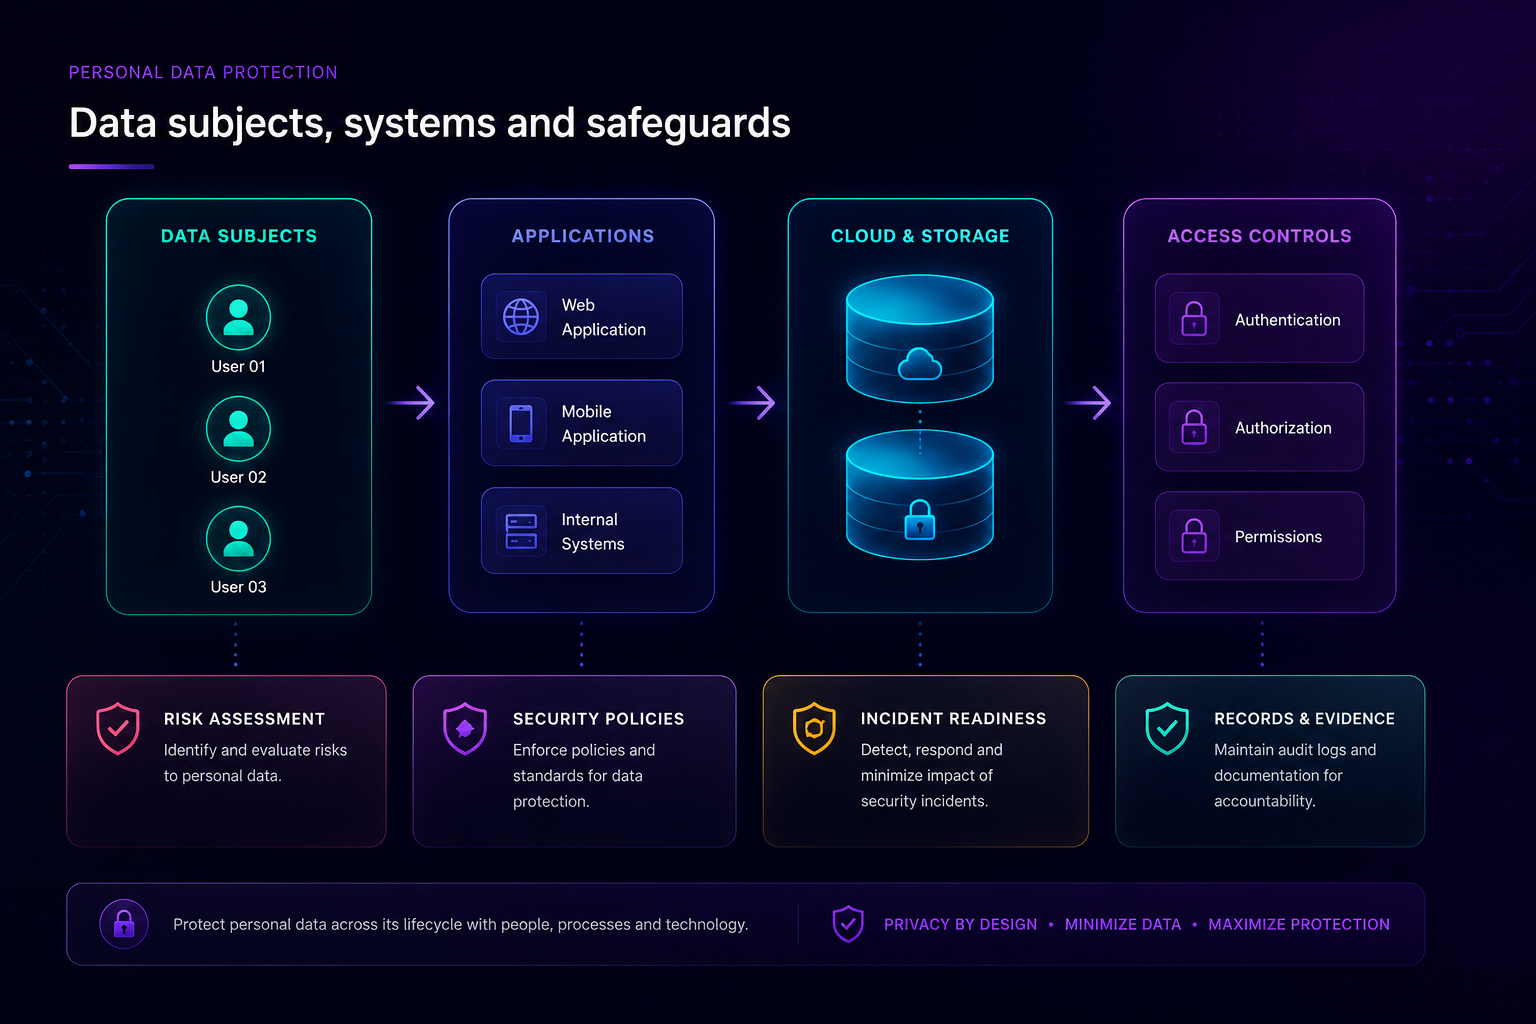
The security layer of data protection: access controls around personal data, technical safeguards across applications and cloud storage, risk assessment, incident preparedness and the policies and records that evidence them.
Where our role ends. ISO/IEC 27001 certification is awarded by an accredited certification body after an independent audit. PCI DSS validation is carried out through a Qualified Security Assessor or an applicable self-assessment route. GDPR is a regulation rather than a certification, and Cylentrix is not a law firm. We provide readiness, assessment, remediation and audit preparation support: we do not issue certification and do not give legal advice.
02SECURITY AUDIT PROCESS
From assessment to compliance readiness
A repeatable seven-stage method that starts with an honest scope and ends with documentation an auditor or assessor can follow.
01
Scope
Define the systems, processes, locations and requirements that are in scope.
02
Assess
Review the relevant policies, processes and technical controls as they operate today.
03
Identify Gaps
Record the areas that may require improvement, with the reasoning behind each one.
04
Prioritize
Rank findings by risk, business impact and compliance relevance rather than by volume.
05
Remediate
Develop practical actions and owners to address the gaps that were identified.
06
Validate
Review remediation progress and control effectiveness where validation is applicable.
07
Prepare
Support documentation and evidence readiness for the relevant audit or assessment.
Completing this process supports preparation and improves readiness. It does not by itself result in certification, attestation or regulatory approval, which remain decisions for the relevant certification body, assessor or authority.
03WHAT YOU GET
Findings you can act on, evidence that holds up
A useful compliance assessment ends with a sequenced plan a team can actually deliver, not a spreadsheet of findings nobody owns.
Compliance gap assessment
An evidenced view of where controls, process or documentation fall short of the requirements in scope, with the reasoning behind each finding.
Risk-based prioritization
Findings ranked by risk exposure, business impact, regulatory relevance, system criticality and implementation effort, so the highest-exposure items move first.
Remediation roadmap
Actions with owners, dependencies and sequencing, phased across near, medium and longer term, costed against the effort your team can realistically absorb.
Evidence readiness
Policies, access reviews, monitoring records, risk registers and configuration history located and structured, so audit preparation stops being a document hunt.
Continuous compliance
Assess, improve, monitor, review, reassess. Periodic reviews and control monitoring keep the position current between formal assessment cycles.
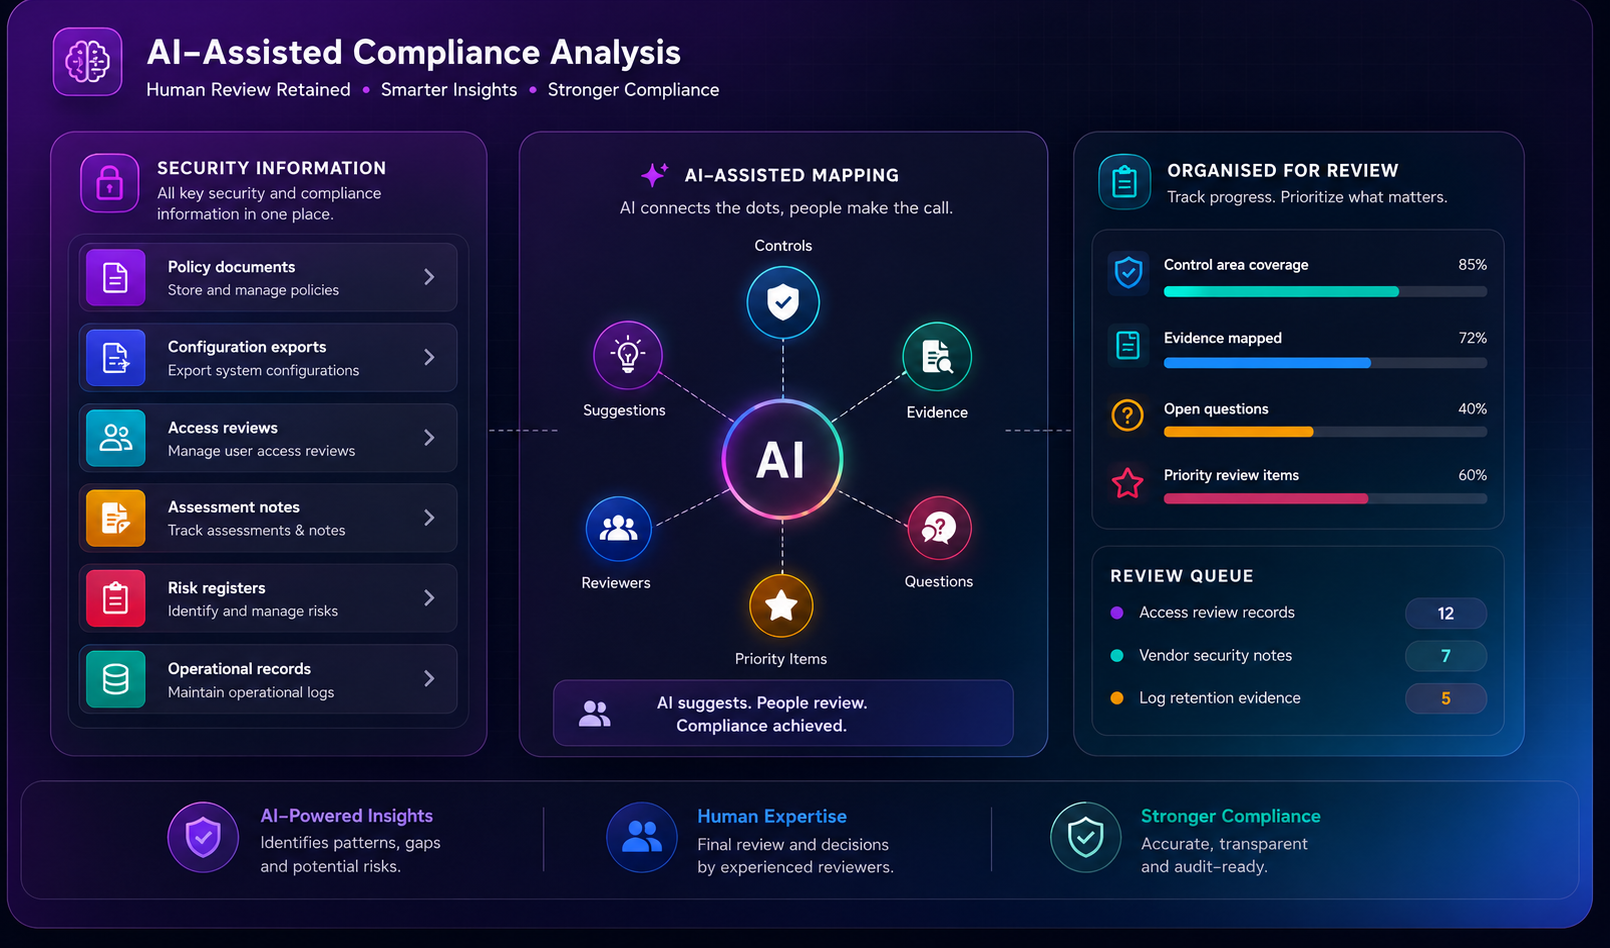
AI-assisted analysis
AI-assisted mapping helps organise large volumes of documentation and match evidence to control areas. Suggestions are reviewed by people, and accountability stays with them.
AI-assisted analysis organises the evidence; people make the call
Evidence should reflect what genuinely happens in the environment. Cylentrix helps organisations locate, structure and improve real records. We never create or backdate evidence, and AI does not determine compliance or replace auditors, compliance professionals or legal counsel.
04INDUSTRIES
Industries where audit readiness matters
Wherever sensitive information, payment environments or prescribed security requirements are involved, an organisation has to be able to show how its controls work, not just say that they do.
Why enterprises choose Cylentrix for security audits & compliance
Assessment is only useful if the people doing it understand how the controls actually run. Cylentrix brings cybersecurity, managed IT and telecom engineering into the same review, so findings are technically grounded and the remediation plan is deliverable.
Cybersecurity, IT and telecom in one team
We assess controls across security, infrastructure and connectivity together, because gaps usually sit in the seams between them.
Real control understanding
Our assessors work with the same technologies they review, so questions go past the checklist to how a control behaves in production.
Enterprise-scale assessment
Multi-site, multi-country and hybrid environments are assessed as one estate rather than as a series of disconnected reviews.
Risk-based approach
Findings are weighted by exposure and business impact, so effort goes where it reduces real risk rather than where it is easiest to log.
Multi-framework readiness
ISO/IEC 27001, PCI DSS and GDPR security requirements are assessed against one control set, so overlapping work is done once.
Technical and governance perspective
Board-level governance language and engineering detail come from the same engagement, so both audiences get what they need.
Practical remediation guidance
Recommendations account for cost, effort and operational impact, and we can support the implementation work where you need hands.
Evidence readiness support
We help structure the records that demonstrate control operation, so audit preparation stops being a last-minute document hunt.
India, USA and Singapore presence
Assessment and advisory delivered across our three operating regions, with consistent method and local working hours.
06TECHNOLOGY & SECURITY PARTNERS
Technology & security partners
Assessment findings often point at tooling. Cylentrix works with established security vendors so remediation can be implemented, not just recommended.
Security platforms we assess, deploy and support
FortinetNetwork security and firewall platforms
Palo Alto NetworksNetwork, cloud and endpoint security
SophosEndpoint, network and managed detection
Check PointNetwork security and threat prevention
07WHITEPAPERS & RESOURCES
Practical guides for compliance readiness
Working guides written by the Cylentrix security governance practice for the teams who will own the controls. These are Cylentrix publications and are not official ISO, PCI Security Standards Council or regulatory documents.
The questions security, IT and governance leaders ask before starting an assessment, answered without the legal hedging.
What is a security compliance audit?
A security compliance audit is a structured review of an organisation's policies, processes and technical controls against a defined set of requirements, such as ISO/IEC 27001, PCI DSS or an internal security standard. It establishes what is in place, how controls operate in practice, what evidence exists to demonstrate them, and where gaps remain. The output is a documented view of current state plus a prioritized list of improvements.
What is an ISO 27001 readiness assessment?
An ISO 27001 readiness assessment reviews an organisation's Information Security Management System against the structure and control areas of ISO/IEC 27001 before a formal certification audit. It typically covers scope definition, information security risk assessment, policy and process documentation, control implementation and the evidence an auditor would expect to see. The result is a gap list and a practical plan to close it.
Does ISO 27001 compliance mean an organisation is automatically certified?
No. Aligning with ISO/IEC 27001 and being certified against it are different things. Certification is awarded by an accredited certification body after an independent audit of the Information Security Management System. Readiness and gap assessment work helps an organisation prepare for that audit, but it does not grant, replace or guarantee certification. Cylentrix provides readiness, assessment and remediation support only.
What is PCI DSS compliance readiness?
PCI DSS compliance readiness is preparation work carried out before a formal PCI DSS validation. It usually starts with understanding scope, which systems store, process or transmit cardholder data and which connected systems fall in scope, then reviews the relevant security controls, identifies gaps and organises supporting evidence. Formal validation is performed through a Qualified Security Assessor or an applicable self-assessment process, depending on the organisation's circumstances.
Does every organisation need PCI DSS compliance?
No. PCI DSS applies to organisations involved in storing, processing or transmitting payment card data, and to certain connected systems. Whether it applies, and which validation route is relevant, depends on the organisation's role, its payment environment, transaction volumes and the requirements set by its acquirer or the payment brands. Organisations with no exposure to cardholder data are generally out of scope.
How does GDPR relate to information security?
GDPR sets requirements for the protection and processing of personal data, and security of processing is one important part of that. Access control, data protection measures, risk assessment, incident preparedness, security policies and supporting records all contribute to an organisation's data protection posture. GDPR is a regulation rather than a certification, and legal interpretation should involve legal counsel or a Data Protection Officer.
What is a compliance gap assessment?
A compliance gap assessment compares the current state of an organisation's controls, processes and documentation against a selected set of requirements and records where the two do not yet meet. A useful gap assessment does more than list findings: it prioritizes them by risk, business impact, regulatory relevance, system criticality and implementation effort, so improvement work can be planned realistically.
How can Cylentrix help with security audits and compliance readiness?
Cylentrix supports enterprises with current-state security assessment, control review, compliance gap assessment against ISO/IEC 27001, PCI DSS and GDPR security requirements, evidence and documentation readiness, prioritized remediation planning and audit preparation. Our teams combine cybersecurity, managed IT and telecom experience across India, USA and Singapore, so recommendations reflect how controls behave in real infrastructure. Cylentrix does not award certification and does not provide legal advice.
09TALK TO A SECURITY EXPERT
Tell us your scope and we will map the work
Share the frameworks you are working to and the environment in scope. A Cylentrix security consultant will come back with an assessment approach, indicative timeline and the effort involved.
A consultant reviews your requirement, not an automated reply
Scoping discussion covering ISO/IEC 27001, PCI DSS or GDPR readiness
Clear next steps and an indicative timeline, with no obligation
India · USA · SingaporeResponse within one business day
Submitting this form sends your enquiry to the Cylentrix security team. Prefer to talk first? Visit our contact page.
GET STARTED
Know where your security stands
Assess your security controls, identify compliance gaps and build a practical roadmap toward stronger security governance and audit readiness. Tell us your scope and the requirements you are working to, and we will come back with an assessment approach and timeline. You can also explore VAPT & red teaming, managed SOC and identity & access management.