VAPT & Red Teaming Services for Proactive Security Validation
Cylentrix VAPT services combine vulnerability assessment and penetration testing to identify exploitable weaknesses and validate your security controls, while authorised Red Teaming simulates realistic attack scenarios before real attackers can exploit them. Every engagement is scoped, controlled and conducted with client approval, ending in risk-based findings your teams can act on, remediate and retest.
Two disciplines, one goal: proving what an attacker could actually do to your organisation, safely and with authorization, so you can fix it first.
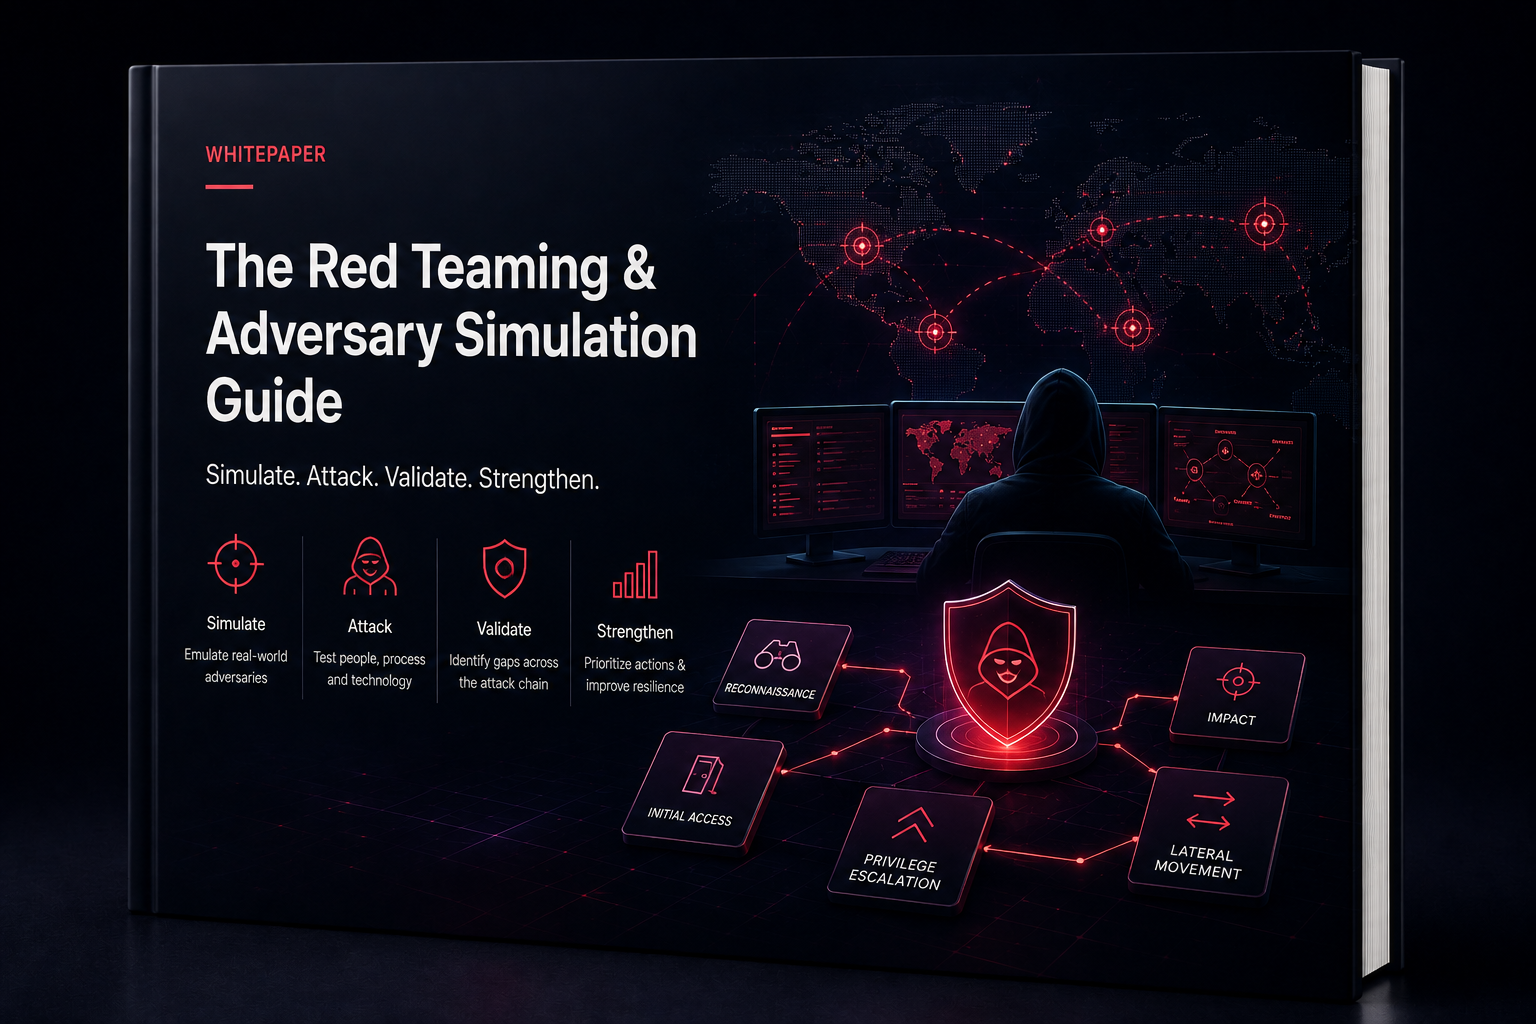
VAPT (Vulnerability Assessment and Penetration Testing) identifies security vulnerabilities across your applications, networks and infrastructure, then validates whether those weaknesses can genuinely be exploited, so remediation effort goes where the real risk is. Red Teaming goes further: an authorised red team simulates realistic attack scenarios against agreed objectives to assess how effectively your organisation can prevent, detect and respond to an attack, exercising people, processes and technology together.
VAPT
Vulnerability Assessment & Penetration Testing
Breadth-first: find, validate and prioritise exploitable weaknesses across defined systems.
Identify vulnerabilities
Assess technical weaknesses
Validate exploitability
Prioritise findings and support remediation
Retest fixes
RED TEAMING
Adversary Simulation
Depth-first: simulate realistic attack paths toward objectives to test prevention, detection and response.
Simulate realistic adversaries
Test attack paths across the environment
Evaluate security controls
Assess detection and response
Validate overall resilience
VAPT = FIND & VALIDATE WEAKNESSES
RED TEAM = SIMULATE & TEST REAL-WORLD ATTACK PATHS
02COVERAGE & APPROACH
Test your security across the attack surface
One engagement partner across every layer an attacker can reach, working to a disciplined path that ends only when remediation is verified.
Web Application VAPT
Identify vulnerabilities in web applications and supporting components through structured assessment and penetration testing.
API Security Testing
Assess APIs for authentication, authorization, data exposure and other security weaknesses across endpoints and integrations.
Network Penetration Testing
Assess internal and external network infrastructure for exploitable weaknesses, misconfigurations and unsafe exposure.
Cloud Security Testing
Evaluate cloud configurations, exposure and security controls across your approved cloud environments and workloads.
Mobile Application Testing
Assess mobile applications and their supporting APIs for security weaknesses in data handling, sessions and access.
Infrastructure Security Assessment
Evaluate servers, network devices and infrastructure components for vulnerabilities and hardening gaps.
External Attack Surface Assessment
Identify publicly exposed assets, services and potential attack paths visible to attackers on the internet.
Configuration & Control Review
Identify security gaps in configurations and defensive controls so hardening keeps pace with the threat landscape.
ENGAGEMENT PROCESS
From discovery to verified security
01
Scope
Define objectives, assets, rules of engagement and testing boundaries with your stakeholders.
02
Discover
Map the approved attack surface and identify the assets relevant to the engagement.
03
Assess
Identify vulnerabilities, weaknesses and configuration issues across the agreed scope.
04
Test
Safely validate exploitable weaknesses, including authorised Red Team attack-path simulation.
05
Validate
Assess the potential impact of confirmed weaknesses and the effectiveness of security controls.
06
Report
Deliver clear findings with evidence, risk ratings and practical recommendations.
07
Remediate
Support your teams in addressing identified weaknesses with actionable guidance.
08
Retest
Validate whether remediation has effectively resolved each identified issue.
AUTHORISEDCONTROLLEDSCOPEDCLIENT-APPROVED
03OUTCOMES & BUSINESS VALUE
Findings that security teams can act on
Every engagement ends in outcomes the business can measure: clear risk visibility for leadership, prioritised fixes for engineering and verified closure. AI-assisted security analysis can help teams prioritize findings and identify patterns across large security datasets.
Risk Visibility for Leadership
An executive summary of security posture, key risks and priorities in business language, ready for the board.
Prioritised Remediation Effort
Findings rated by risk and exploitability, so engineering time goes to the issues that actually matter.
Evidence-Backed Findings
Clear, reproducible evidence for each confirmed weakness, so no finding is disputed or double-checked twice.
Actionable Fix Guidance
Practical, prioritised fixes your engineering and operations teams can implement without further consulting.
Verified Closure
Fixed findings are retested and their closure verified, giving auditors and stakeholders proof, not promises.
EACH FINDINGFinding→Risk→Affected Asset→Evidence→Business Impact→Recommended Remediation
04INDUSTRIES
Industries that test their defenses before attackers do
Wherever sensitive data, payments or critical operations live, exploitable weaknesses carry a price tag. Cylentrix delivers VAPT and Red Teaming for the industries attackers target first.
Why enterprises choose Cylentrix for VAPT & Red Teaming
Security testing is only useful if it reflects how your enterprise actually runs. Cylentrix tests with the perspective of a partner that designs, secures and operates enterprise technology every day.
Cybersecurity + IT + Telecom depth
One practice spanning security, managed IT and enterprise networks, so testing reflects how your systems really connect and operate.
Application & infrastructure testing
Web, API, network, cloud, mobile and infrastructure assessed by one team, so weaknesses that cross layers don't fall between vendors.
Attack-surface perspective
Engagements start from what an attacker can actually see and reach, not from an inventory list, so effort lands on real exposure.
Risk-focused findings
Findings are rated by genuine business risk and exploitability, so a long report never buries the handful of issues that matter.
Actionable remediation guidance
Every finding ships with practical, prioritised remediation steps that your engineering and operations teams can implement.
Security-control validation
Testing measures whether your preventive and detective controls actually work under simulated attack, not just whether they exist.
Retesting & verification
Remediated findings are retested and formally verified as closed, so the engagement ends with evidence rather than assumptions.
Enterprise engagement approach
Defined scope, written authorization, controlled execution and stakeholder coordination from kickoff through retest.
India, USA & Singapore presence
Engagement teams that work across time zones and regions, aligned with the way multinational enterprises operate.
06PARTNERS
Technology & security partners
Cylentrix works alongside established technology and security platforms so testing insight translates into hardened, well-configured defenses.
07WHITEPAPERS & RESOURCES
Understand security testing before you commission it
Practical guides from the Cylentrix security practice, written for the leaders who will own the findings, the fixes and the risk.
Tell us what you need tested: web applications, APIs, networks, cloud, mobile or a full adversary simulation. A Cylentrix security specialist will come back with a scoped approach, not a sales pitch.
Scoping call to agree assets, objectives and rules of engagement
Written authorization and a defined testing window before any activity
Risk-rated findings, remediation guidance and a retest to verify closure
RESPONSE WITHIN 1 BUSINESS DAY · NDA AVAILABLE ON REQUEST
ENGAGEMENT ENQUIRY
Request a VAPT or Red Team quote
09FAQ
VAPT & Red Teaming, answered directly
The questions security and IT leaders ask before commissioning a security testing engagement, answered the way our security engineers answer them.
What is VAPT?
VAPT stands for Vulnerability Assessment and Penetration Testing. A vulnerability assessment identifies security weaknesses across applications, networks and infrastructure, while penetration testing safely validates whether those weaknesses can actually be exploited. Together they show an organisation what is exposed, what is exploitable and what to fix first.
What is the difference between vulnerability assessment and penetration testing?
A vulnerability assessment is broad: it discovers and lists potential weaknesses across the environment. Penetration testing is deep: skilled testers safely attempt to exploit selected weaknesses within an agreed scope to confirm real-world impact. Assessment answers what could be wrong; penetration testing answers what an attacker could actually do.
What is Red Teaming?
Red Teaming is an authorised, goal-driven simulation of a realistic attacker. Instead of listing vulnerabilities, a Red Team engagement tests whether an organisation can prevent, detect, investigate and respond to an attack against agreed objectives, exercising people, processes and technology together under strict rules of engagement.
What is the difference between VAPT and Red Teaming?
VAPT focuses on finding and validating as many exploitable weaknesses as possible in defined systems. Red Teaming focuses on simulating realistic attack paths toward specific objectives to test detection and response. VAPT measures how exposed you are; Red Teaming measures how well your defenses hold up when tested.
What systems can be included in a VAPT engagement?
A VAPT engagement can cover web applications, APIs, internal and external networks, cloud environments, mobile applications, servers and infrastructure components, and the externally exposed attack surface. Scope is agreed with the client before testing begins, and only approved assets are assessed.
How does Red Teaming test an organisation's security controls?
Within an agreed scope, the Red Team simulates realistic attack scenarios across phases such as reconnaissance, initial access, privilege escalation and lateral movement toward defined objectives. The engagement evaluates whether preventive controls block the activity, whether monitoring detects it, and how effectively security teams investigate and respond.
Is VAPT or Red Teaming performed safely and with authorization?
Yes. All Cylentrix security testing is conducted only with explicit written client authorization, within a defined scope and agreed rules of engagement. Testing is controlled to avoid disruption, sensitive findings are handled confidentially, and activity is coordinated with client stakeholders throughout the engagement.
How can Cylentrix help with VAPT and Red Teaming?
Cylentrix scopes, executes and reports authorised VAPT and Red Team engagements across web, API, network, cloud, mobile and infrastructure, then supports remediation and retests fixes to verify closure. Engagements draw on Cylentrix's combined cybersecurity, IT and telecom practice across India, USA and Singapore.
GET STARTED
Find the weaknesses before they become breaches
Validate your security posture, uncover exploitable weaknesses and strengthen your defenses with focused VAPT and authorised Red Teaming engagements. Also explore our Managed SOC, SIEM & SOAR and Zero Trust Architecture services.