Cylentrix

SOC OPERATIONAL • 24/7 India • USA • Singapore
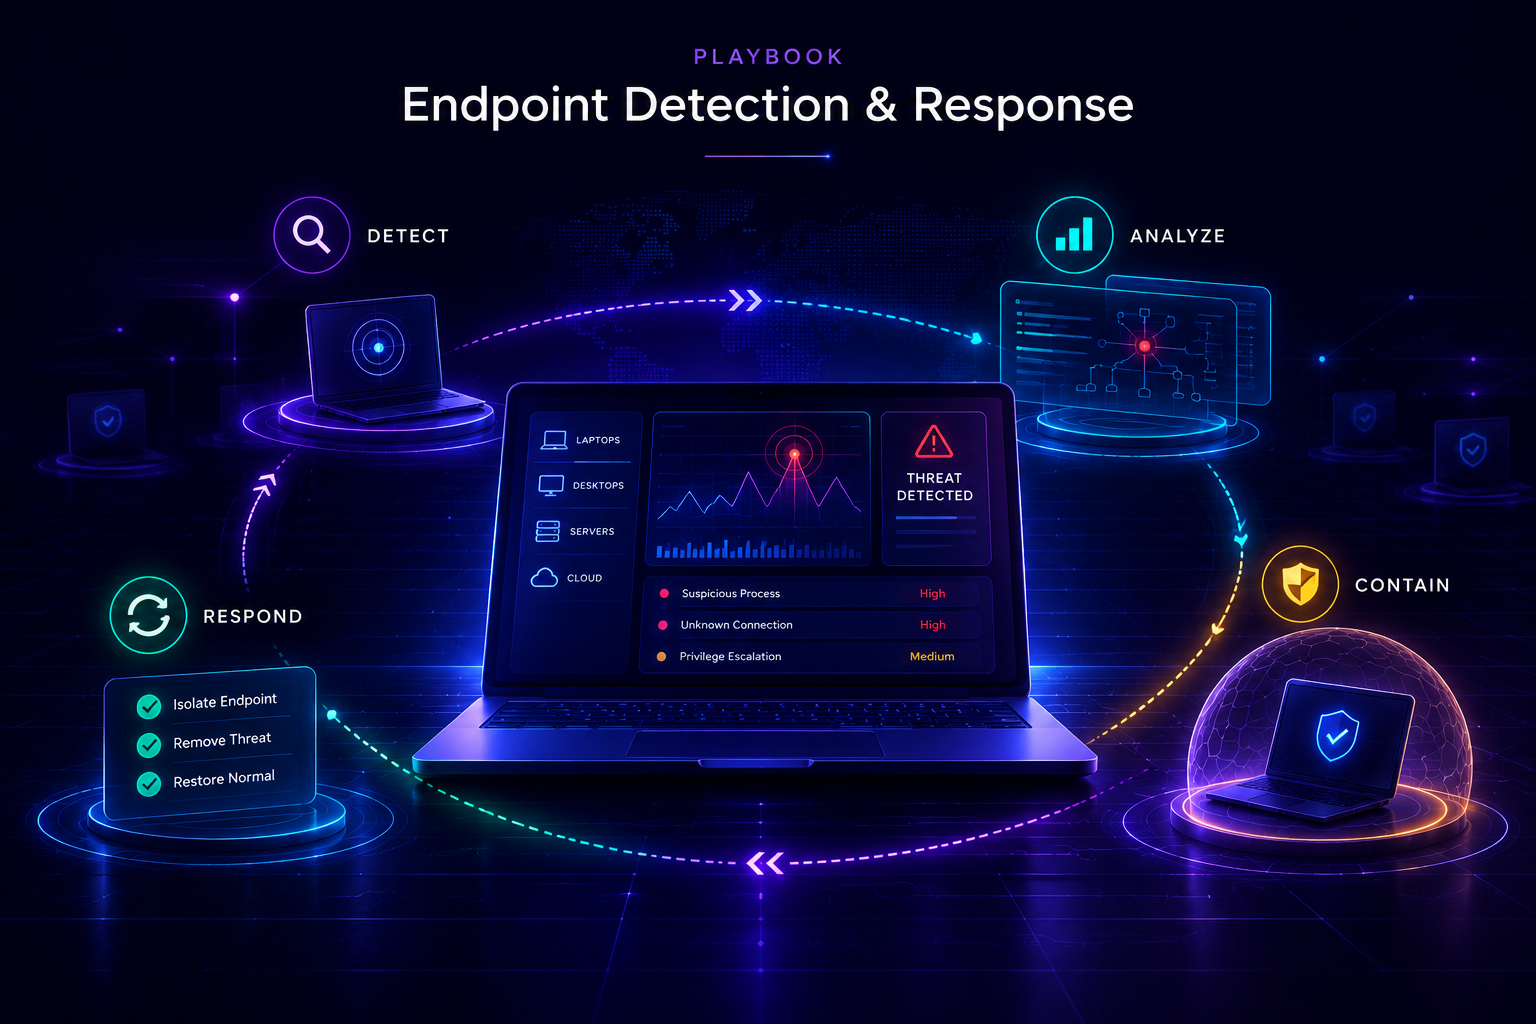
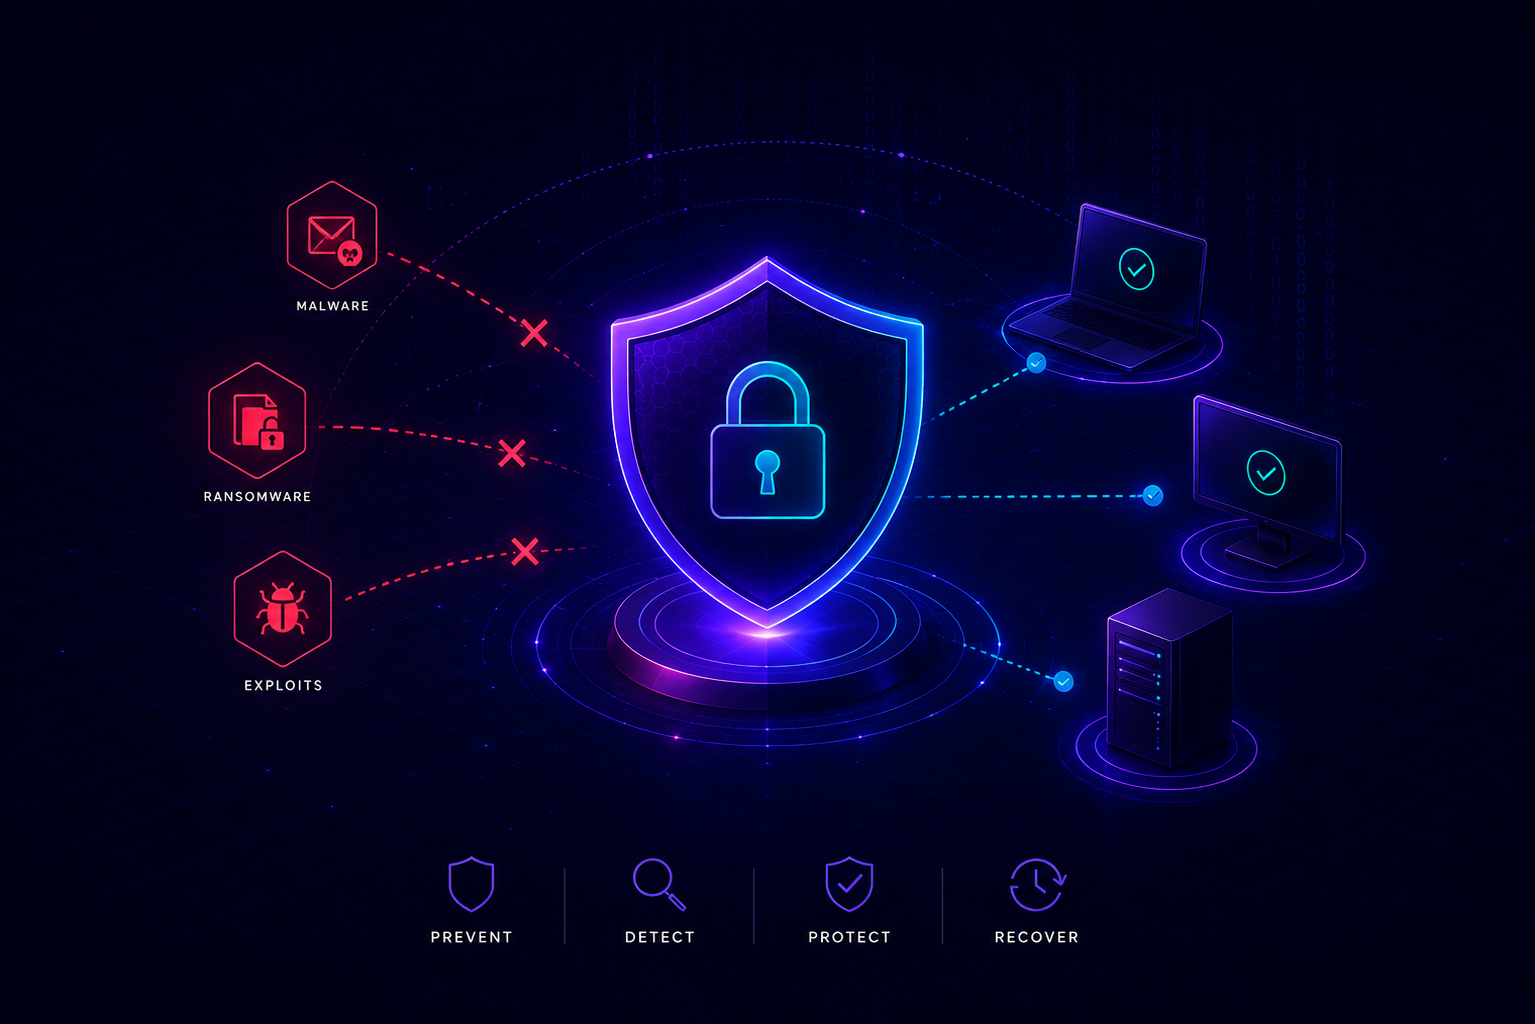
Enterprise EDR dashboard showing endpoint threat detection, contained incidents and 24/7 endpoint monitoring across a global estate
CYBERSECURITY · ENDPOINT SECURITY

Endpoint Security & EDR
for Advanced Threat
Detection and Response

Protect laptops, desktops, servers and other endpoints with continuous visibility, behavioral threat detection and rapid response capabilities designed to identify and contain modern cyber threats. Cylentrix delivers Endpoint Security and EDR services that surface malware, ransomware and suspicious endpoint activity early, support investigation of what actually happened, and contain affected devices before an incident spreads.

  • 24×7Endpoint Monitoring
  • ManagedEDR Services
  • BehaviorBased Detection
  • RapidContainment
  • ThreatHunting
  • 3Country Presence
01ENDPOINT SECURITY & EDR

Secure Every Endpoint.
Detect Every Threat.

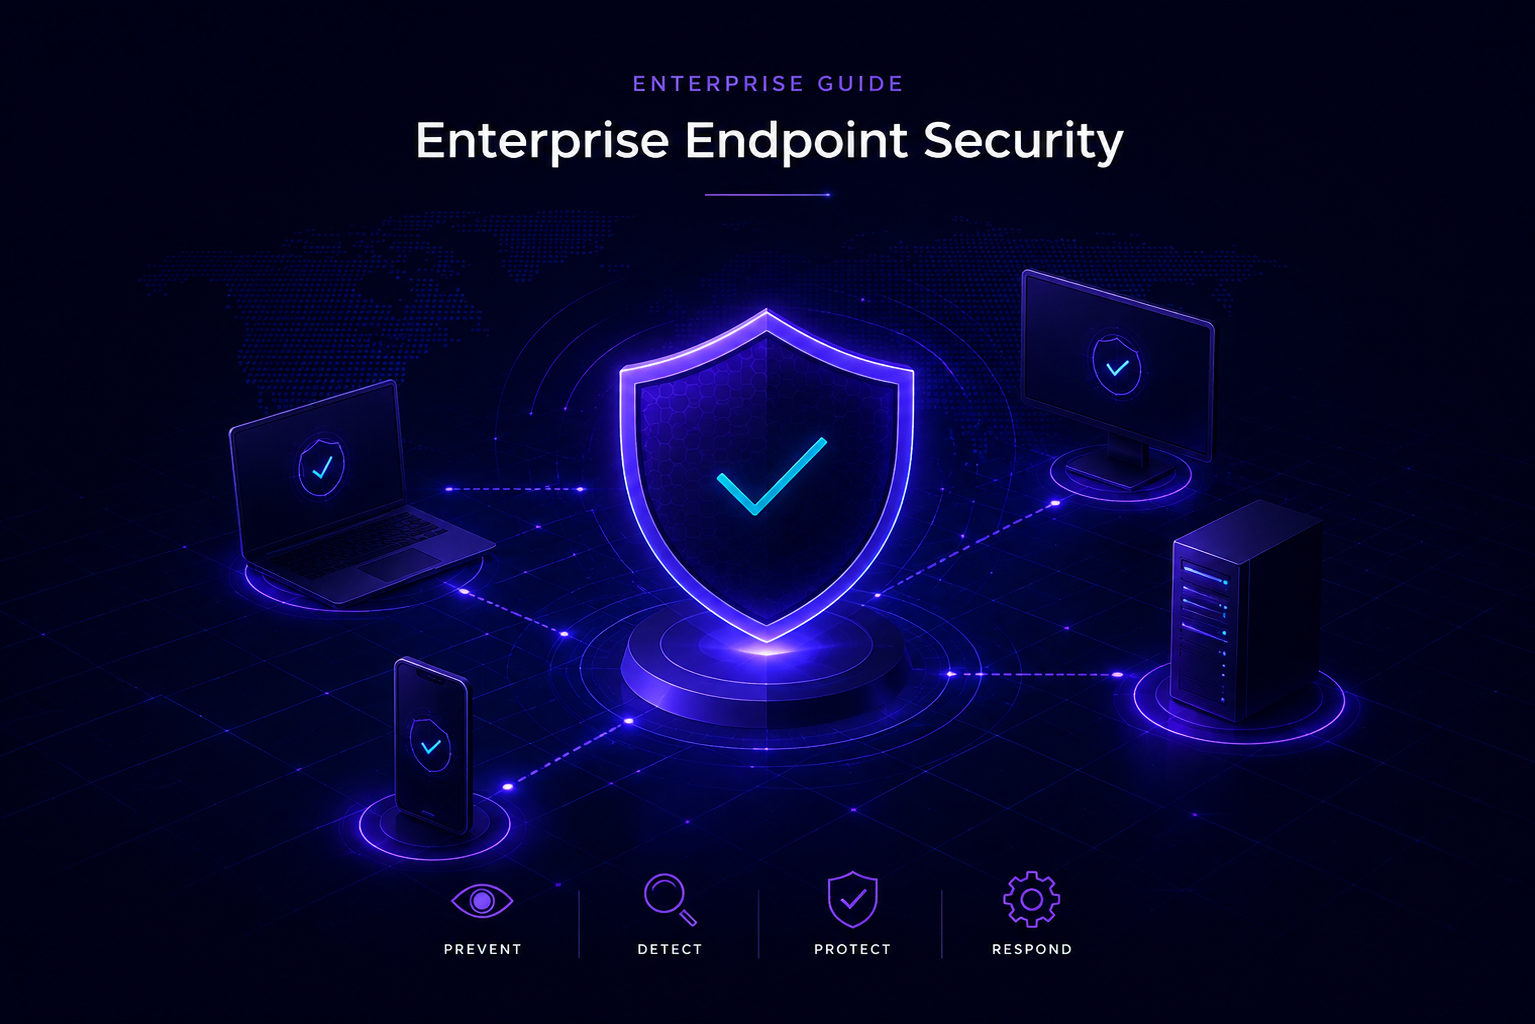
Endpoint Security protects the device. EDR records what happens on it. Together they give security teams the visibility to detect, investigate and respond to threats that reach the endpoint.

Endpoints are where people, data and applications meet, which makes them the most common entry point into an enterprise. Malware, ransomware, credential theft, phishing payloads, malicious applications, unauthorised access and lateral movement almost always begin on a device somebody is using.

Endpoint protection blocks what is already known to be malicious. Endpoint Detection and Response adds what matters next: continuous recording of endpoint activity, behavior-based detection of the activity a signature would miss, and the investigation and response capability a security team needs to act on it quickly.

  • Malware
  • Ransomware
  • Credential theft
  • Phishing payloads
  • Malicious applications
  • Unauthorised access
  • Lateral movement
  • Continuous Endpoint Visibility

    Endpoint activity is recorded continuously, so security teams can see what ran, when and under which user.

  • Behavior-Based Detection

    Suspicious sequences of behavior are flagged even when the file, script or tool involved has never been seen before.

  • Rapid Investigation

    Process chains, files, users and connections are traceable, turning an alert into an understood sequence of events.

  • Response & Containment

    Affected endpoints can be isolated and remediated so a single compromised device does not become an enterprise incident.

02HOW EDR WORKS

From Endpoint Activity
to Rapid Response

EDR turns raw endpoint telemetry into a decision. Activity is collected, analyzed and detected on, then investigated, contained and resolved.

Endpoint telemetry collected

  • Processes
  • Files
  • Network Connections
  • Users
  • Applications
  • System Activity
  • Device Behavior
  • Source

    Endpoint Activity

    Users, processes and applications generate activity on every device.

  • Step 01

    Collect

    Lightweight agents record endpoint telemetry continuously.

  • Step 02

    Analyze

    Activity is correlated and compared against known and abnormal behavior.

  • Step 03

    Detect

    Suspicious behavior and indicators of compromise raise a detection.

  • Step 04

    Investigate

    Analysts trace the processes, files, users and connections involved.

  • Step 05

    Contain

    Affected endpoints can be isolated to stop a threat spreading further.

  • Step 06

    Respond

    Malicious processes and artefacts are removed and access is revoked.

  • Step 07

    Recover

    The endpoint is restored, hardened and returned to normal operation.

EDR Analytics Threat Detection Security Decision Response Action
03DETECTION & RESPONSE

See the Attack. Understand
the Threat. Take Action.

What endpoint detection and response actually gives a security team: the sequence of events, the affected device, and a way to stop it.

  • Detect suspicious behavior

    Endpoint behavior that deviates from normal is surfaced as a detection, not left in a log.

  • Investigate attack activity

    Recorded telemetry shows what executed, under which account, and in what order.

  • Trace processes and connections

    Parent and child processes, file writes and outbound connections are followed end to end.

  • Identify indicators of compromise

    Files, hashes, registry changes and network indicators are captured for hunting across the estate.

  • Isolate affected endpoints

    A compromised device can be cut off from the network while remaining reachable for investigation.

  • Support remediation and recovery

    Artefacts are removed, credentials rotated and the endpoint is returned to a trusted state.

05WHY CYLENTRIX

Why enterprises choose
Cylentrix for Endpoint
Security & EDR

Endpoint security is only as good as the team operating it. Cylentrix combines cybersecurity, managed IT and telecom engineering, so detection is designed around the infrastructure it runs on.

Cybersecurity, IT and telecom in one team

The people securing your endpoints also understand your network, identity and infrastructure — no handoff between vendors when something moves fast.

Enterprise endpoint visibility

Laptops, desktops, servers, remote devices and branch endpoints are covered under one view rather than several disconnected consoles.

Behavior-based threat detection

Detection engineering tuned to your environment, so behavioral alerts reflect how your users and applications actually operate.

Managed EDR operations

Deployment, policy tuning, monitoring and continuous improvement of your EDR platform run as an ongoing managed service.

Proactive threat hunting

Regular hunts across endpoint telemetry look for indicators of compromise and quiet activity that has not yet triggered an alert.

Incident response support

When a detection becomes an incident, the same team investigates, contains, remediates and documents what happened.

Integrated with security operations

Endpoint detections feed your wider security operations and SIEM workflows instead of sitting isolated in a separate tool.

Enterprise infrastructure understanding

Rollouts account for servers, VDI, branch sites, bandwidth and change windows, so agents land without breaking operations.

India, USA and Singapore presence

Distributed delivery across three regions supports enterprises with endpoints and users spread across multiple time zones.

06PARTNERS

Technology &
Security Partners

Cylentrix deploys and operates endpoint protection and EDR platforms from established security vendors, selected to fit each environment rather than a single fixed stack.

  • CrowdStrike Endpoint protection and EDR platform
  • ManageEngine Endpoint management and IT security tooling
08FAQ

Endpoint Security & EDR,
answered directly

The questions security and IT leaders ask before selecting an endpoint security and EDR service.

What is Endpoint Security?

Endpoint Security is the protection of devices such as laptops, desktops, servers and other endpoints against malware, malicious files, unauthorised access and suspicious activity. It combines preventive controls on the device with policy enforcement, so known threats are blocked before they execute. It is the layer that protects the point where users, data and applications meet.

What is EDR?

EDR stands for Endpoint Detection and Response. An EDR agent continuously records endpoint activity — processes, files, users, applications and network connections — and analyses it for suspicious behavior. When something is detected, EDR gives security teams the visibility to investigate what happened and the capability to respond, including isolating the affected endpoint.

What is the difference between Endpoint Security and EDR?

Endpoint Security is mainly preventive: it blocks known malicious files and activity on the device. EDR is detective and responsive: it records endpoint activity, detects suspicious behavior that prevention missed, and supports investigation and containment. Most enterprises run both — endpoint protection to stop what is known, EDR to catch and respond to what is not.

How does EDR detect threats?

EDR detects threats by analysing behavior rather than relying only on signatures. Endpoint telemetry is collected continuously and correlated to identify suspicious sequences: an unusual parent-child process chain, an unexpected script interpreter, abnormal file activity or an outbound connection to an unknown host. Detection rules, threat intelligence and AI-assisted behavioral analytics work together, and analysts validate what is raised.

Can EDR detect ransomware and malware?

Yes. EDR is designed to detect the behaviors associated with ransomware and malware — suspicious process execution, rapid or unusual file modification, attempts to disable recovery options and unexpected outbound communication. Because detection is behavior-based, EDR can surface activity from malware variants that no signature has seen yet, and support containment before it spreads.

Can EDR monitor remote and distributed endpoints?

Yes. EDR agents report to a cloud-managed platform, so endpoint monitoring continues whether the device is in the office, at a branch, at home or travelling. Remote and distributed endpoints are covered by the same detection logic and response capability, including the ability to isolate a device that is off the corporate network.

Can EDR integrate with SIEM and SOC environments?

Yes. EDR detections and endpoint telemetry can be forwarded to a SIEM and consumed by SOC workflows, so endpoint activity is correlated with network, identity and cloud events. This gives analysts a single investigation timeline instead of a separate endpoint silo, and lets response actions be triggered as part of established security operations processes.

How can Cylentrix help with Endpoint Security and EDR?

Cylentrix designs, deploys and operates endpoint security and managed EDR services for enterprises across India, USA and Singapore. That includes agent rollout across laptops, desktops and servers, detection tuning for your environment, continuous endpoint monitoring, threat hunting, investigation support and incident response — integrated with your wider security operations rather than run in isolation.

GET STARTED

Strengthen Every Endpoint
Against Modern Threats

Gain deeper endpoint visibility, detect suspicious activity earlier and strengthen your response to endpoint-based cyber threats with Cylentrix.

  • Endpoint security review of your current laptop, desktop and server estate
  • Managed EDR rollout with detection tuned to your environment
  • Threat hunting, investigation support and incident response
Talk to a Security Expert

Tell us about your endpoint estate and a Cylentrix security specialist will respond with next steps.