Cylentrix

SOC OPERATIONAL • 24/7 India • USA • Singapore
CYBERSECURITY · ENTERPRISE PRACTICE

AI-Powered Cybersecurity
for Modern Enterprises

Cylentrix delivers managed security services that bring Managed SOC, SIEM, MDR and XDR, Zero Trust, endpoint security, network and cloud security, email defence and compliance into one architecture and one SLA. AI-assisted detection filters the noise; certified analysts make the calls. Enterprise protection starts with an assessment of the controls you already own, not a licence quote.
24×7 SOC Zero Trust Managed Security Compliance Ready
01Trust & Assurance

Enterprise Certifications &
Technology Partnerships.

Trusted security standards, cloud partnerships and global compliance certifications behind every managed security engagement.

  • AICPA SOC certification held by Cylentrix
  • SOC 2 Type II certification held by Cylentrix
  • SOC 1 Type II certification held by Cylentrix
  • SOC 3 Certified certification held by Cylentrix
  • MeitY certification held by Cylentrix
  • Uptime Tier IV Ops certification held by Cylentrix
  • Uptime Tier III certification held by Cylentrix
  • OIX-2 Certified DC certification held by Cylentrix
  • Trusted Partner Network certification held by Cylentrix
  • SAP & Oracle certification held by Cylentrix
  • USGBC Member certification held by Cylentrix
  • IGBC certification held by Cylentrix
02What We Do

Security as an operating
discipline.

Eight control surfaces, one architecture, one team that owns the outcome end to end.

Most enterprises do not have a security product problem. They have a coverage problem. Firewalls sit with the network team, endpoints with IT, cloud with a platform team, identity with whoever built the directory. Every control works. Nothing correlates.

Cylentrix treats the enterprise as one attack surface with eight control planes, feeding every plane into a single 24×7 managed SOC. We assess and fix configuration gaps in the controls you already own before proposing a licence, and every engagement carries a named architect, a written SLA and quarterly reviews of coverage and control drift.

Networks

Segmentation, NGFW policy, IDS/IPS and east-west traffic inspection.
Network security control surface: segmentation, NGFW policy and IDS/IPS

Cloud

CSPM, CIEM and workload protection across AWS, Azure and GCP.
Cloud security control surface: CSPM, CIEM and workload protection

Endpoints

EDR/XDR on laptops, servers and containers with behavioural detection.
Endpoint security control surface: EDR and XDR with behavioural detection

Identity

IAM, PAM, MFA and conditional access enforcing least privilege.
Identity control surface: IAM, PAM, MFA and conditional access

Applications

WAF, API protection, SAST/DAST and secure SDLC integration.
Application security control surface: WAF, API protection and secure SDLC

Email

Anti-phishing, BEC defence, DMARC enforcement and URL sandboxing.
Email security control surface: anti-phishing, BEC defence and DMARC

Data

Discovery, classification, DLP and encryption at rest and in transit.
Data security control surface: discovery, classification, DLP and encryption

Infrastructure

Datacentre, OT and hybrid estate hardening with baseline enforcement.
Infrastructure control surface: datacentre, OT and hybrid estate hardening
03Cybersecurity Services

Fifteen capabilities.
Deployed the way you need them.

Take one service to solve a specific gap, or combine several into a managed programme under a single SLA. Each links to full technical detail, scope and deliverables.
Managed SOC services: 24x7 monitoring, triage and response

Managed SOC

24×7 monitoring, triage and response from our Security Operations Centre. Detection engineering mapped to MITRE ATT&CK, with proactive threat hunting on your telemetry.

Learn more
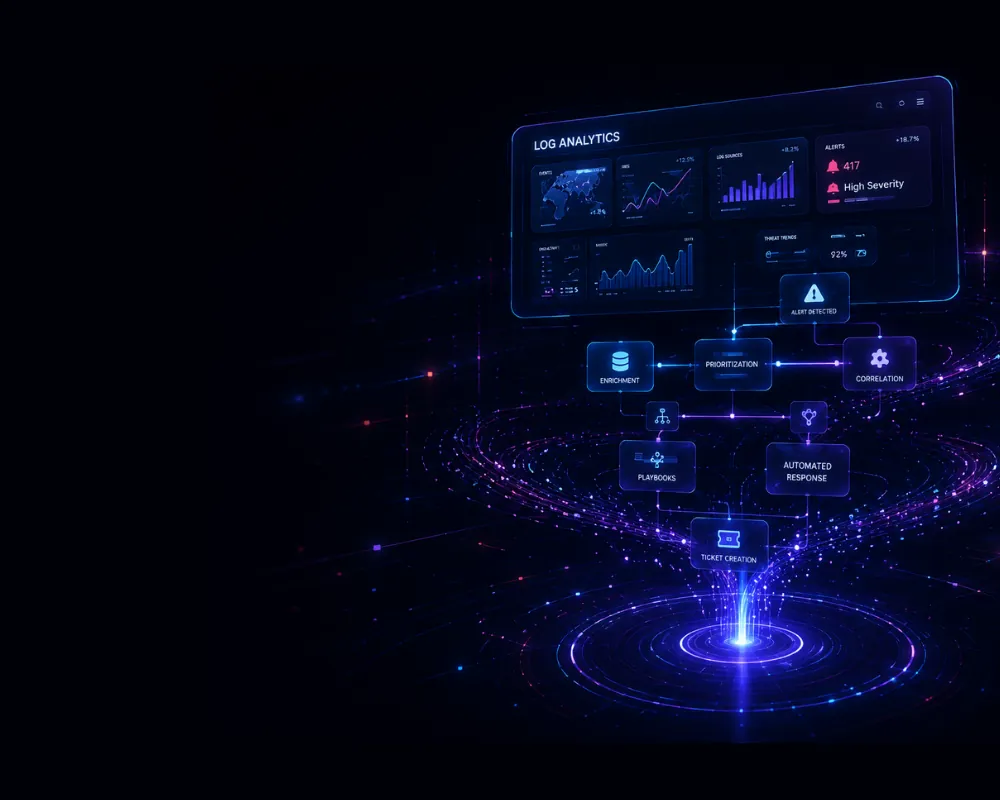
SIEM and SOAR: centralised log collection, correlation and automated playbooks

SIEM & SOAR

Centralised log collection, correlation rules and dashboards, plus automated playbooks that contain routine incidents without waiting for an analyst.

Learn more
Zero Trust architecture with micro-segmentation and continuous verification

Zero Trust Architecture

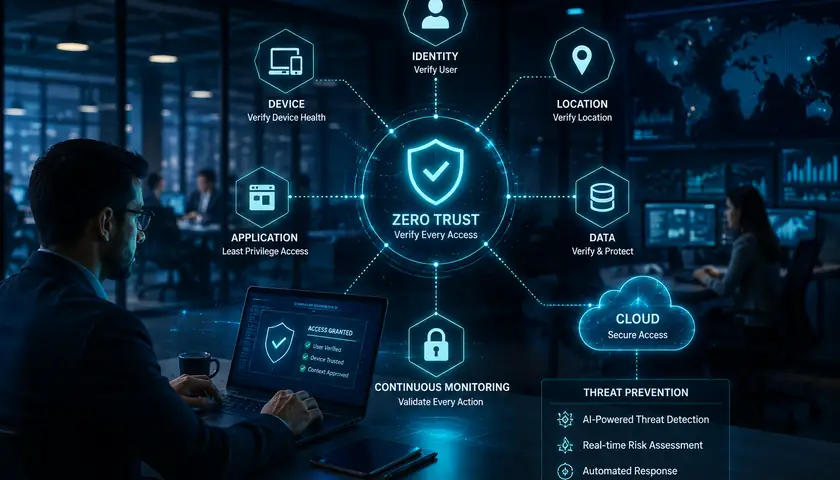
Identity-anchored access with micro-segmentation and continuous verification. Replaces flat VPN trust with per-application, per-session authorisation.

Learn more
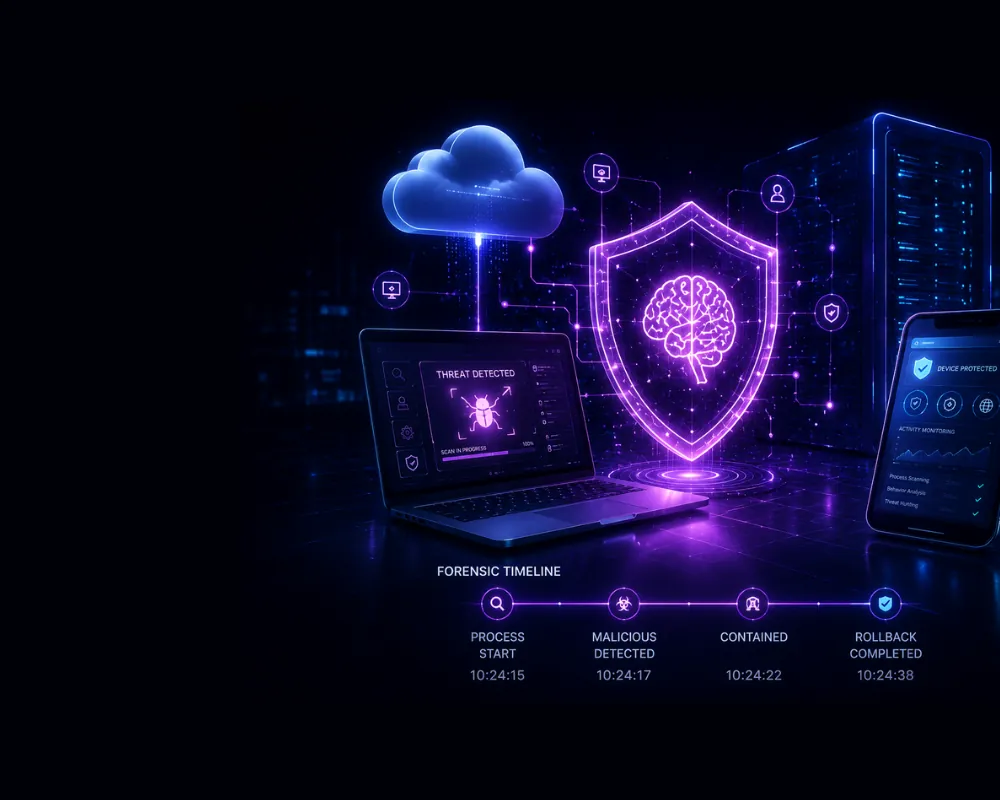
Endpoint security with EDR and XDR across laptops, servers and cloud workloads

Endpoint Security · EDR / XDR

Behaviour-based protection for laptops, servers and cloud workloads, with device isolation, rollback and forensic timeline reconstruction.

Learn more
Next-generation firewall deployment, migration and managed policy

Next-Gen Firewall

Design, deployment, migration and day-two management of Palo Alto, Fortinet, Cisco and Check Point estates, including rulebase cleanup and HA design.

Learn more
Network security: segmentation design, IDS/IPS tuning and NAC

Network Security

Segmentation design, IDS/IPS tuning, NAC and secure remote access, hardening lateral movement paths across campus, datacentre and branch.

Learn more
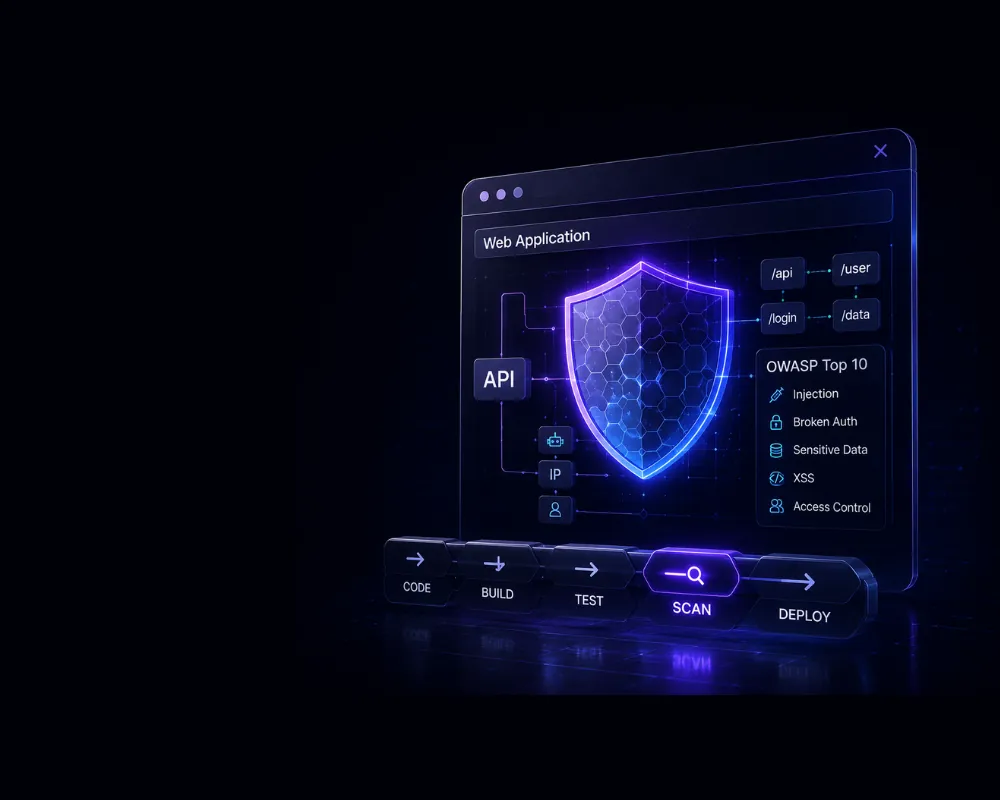
Application security and WAF: API protection, bot mitigation and secure SDLC

Application Security & WAF

Web application firewall tuning, API protection, bot mitigation, and SAST/DAST/SCA wired into your build pipeline rather than bolted on at release.

Learn more
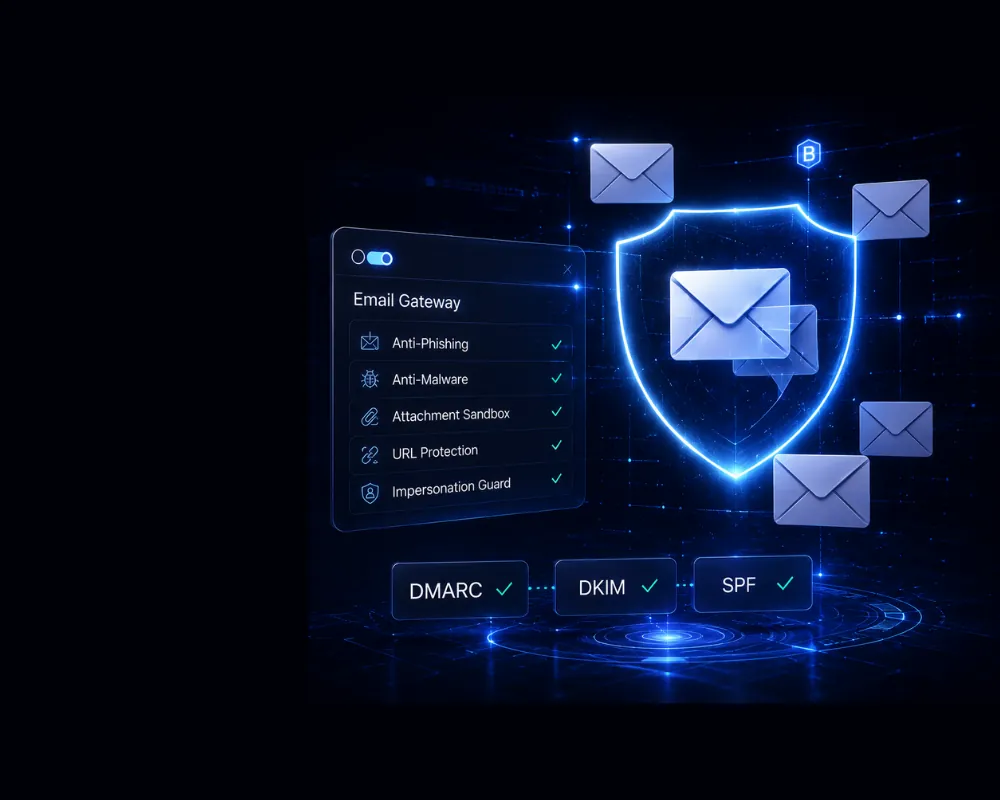
Email security gateway: anti-phishing, BEC defence and DMARC enforcement

Email Security

Phishing, BEC and malware defence at the gateway, with attachment sandboxing, URL rewriting, impersonation controls and DMARC/DKIM/SPF enforcement.

Learn more
Identity and access management: SSO, MFA and access certification

Identity & Access Management

SSO, MFA, lifecycle provisioning and access certification. Consolidates scattered local accounts into governed identity with auditable joiner-mover-leaver flows.

Learn more
Privileged access management: vaulted credentials and session recording

Privileged Access Management

Vaulted credentials, session recording, just-in-time elevation and break-glass workflows for domain admins, root accounts and third-party engineers.

Learn more
VAPT and red teaming: black-box, grey-box and assumed-breach testing

VAPT & Red Teaming

Black-box, grey-box and assumed-breach testing of networks, applications and cloud. Findings arrive with reproduction steps and a prioritised remediation plan.

Learn more
Threat intelligence: curated feeds, dark-web and credential-leak monitoring

Threat Intelligence

Curated feeds, dark-web and credential-leak monitoring for your domains and brand, converted into detection content rather than delivered as a PDF digest.

Learn more
Incident response: same-day mobilisation, forensic imaging and containment

Incident Response

Retained IR with same-day mobilisation, forensic imaging, containment, eradication and a root-cause report suitable for regulators, insurers and the board.

Learn more
Cloud security posture management for AWS, Azure and GCP

Cloud Security

Posture management for AWS, Azure and GCP: CIS benchmark enforcement, entitlement right-sizing, container and Kubernetes hardening, and control-plane monitoring.

Learn more
Security audit and compliance: ISO 27001, SOC 2, PCI-DSS, GDPR and DPDPA readiness

Compliance & Security Audit

ISO 27001, SOC 2, PCI-DSS, HIPAA, GDPR, DPDPA and RBI/SEBI/IRDAI readiness: gap assessment, control design, evidence packs and auditor liaison.

Learn more
04Challenges We Solve

The eight problems
that actually cause breaches.

Select a scenario to see how the risk materialises in a real environment, and the specific controls we put in place to stop it.

Ransomware

The problem

Attackers rarely encrypt on day one. They enter through an exposed service or stolen credential, escalate privilege and delete backups, then detonate outside business hours.

How we solve it

We shorten dwell time: EDR that flags credential dumping and shadow-copy deletion, segmentation that blocks lateral movement, immutable backups proven by restore drill, and a SOC authorised to isolate a host immediately.

EDR / XDRMicro-segmentationImmutable BackupIR Retainer

Phishing & Business Email Compromise

The problem

Modern phishing carries no malware, just a convincing invoice, a payroll change request, or a login page that harvests an MFA token in real time.

How we solve it

Attachment sandboxing, URL rewriting and impersonation detection, backed by enforced DMARC so your domain cannot be spoofed. Phishing-resistant MFA ensures a stolen password alone gets nobody in.

Secure Email GatewayDMARC EnforcementConditional AccessAwareness Simulation

Data Breach & Exfiltration

The problem

Sensitive data spreads far beyond the systems that created it, into spreadsheets, shared drives and test databases. Most organisations cannot say where regulated data actually lives.

How we solve it

Discovery and classification across endpoints, file shares, email and cloud storage, then DLP policy at the egress points that matter. Encryption and access review shrink the blast radius.

Data DiscoveryDLPEncryptionAccess Review

Insider Threat

The problem

Access accumulates. Roles change, projects end and contractors leave, but permissions stay. A departing employee with valid credentials is invisible to controls built to spot outsiders.

How we solve it

Least privilege through PAM with session recording and just-in-time elevation, deprovisioning tied to your HR system, and analytics that flag unusual access against each user's own baseline.

PAMUEBAAccess CertificationSession Recording

Cloud Misconfiguration

The problem

Cloud breaches are configuration failures, not exploits: a public bucket, an over-permissive IAM role, an open security group, logging disabled in a forgotten region.

How we solve it

Continuous posture management against CIS benchmarks across AWS, Azure and GCP, entitlement analysis that strips unused permissions, and infrastructure-as-code guardrails that catch drift at commit.

CSPMCIEMIaC GuardrailsCloudTrail Monitoring

Shadow IT

The problem

Teams adopt SaaS faster than IT can review it. Corporate data lands in unvetted apps with no SSO and no logging, discovered during an incident or an audit.

How we solve it

DNS, proxy and cloud-access telemetry give you an honest inventory of what is in use. From there we sanction, migrate or block, bringing approved tools under SSO and logging.

CASBDNS FilteringSSO OnboardingSaaS Inventory

Compliance & Audit Gaps

The problem

Controls exist but the evidence does not. Teams rebuild the same audit pack each cycle from screenshots, and findings repeat because nothing measures control drift between audits.

How we solve it

We map controls once to the frameworks that apply (ISO 27001, SOC 2, PCI-DSS, RBI and SEBI CSCRF), then automate evidence collection so the pack builds continuously, not under deadline.

Control MappingEvidence AutomationGap AssessmentAuditor Liaison

Remote & Hybrid Workforce Security

The problem

VPN was built to extend the office network, not to gate it. Once a remote device connects it often has broad internal reach, however it is owned or patched.

How we solve it

ZTNA replaces the tunnel with per-application authorisation based on verified identity and live device posture. Managed EDR, encryption and DNS filtering travel with the device.

ZTNADevice PostureManaged EDRDNS Security
05How We Engage

From first assessment
to continuous operation.

A seven-stage delivery cycle with defined artefacts at every stage, so you always know what has been done, what is next, and who owns it.

Discover

Inventory assets, data flows, identities and existing controls. Establish what you actually own before anything is recommended.

Assess

Test the estate against a threat model relevant to your sector. Findings ranked by exploitability and business impact.

Design

Target-state architecture, control mapping and phased roadmap. Deliverables include HLD, LLD and RACI.

Implement

Phased build with controlled cutovers, change governance, testing and knowledge transfer to your team.

Monitor

Telemetry into the SOC, detection content tuned to your environment, and SLA-backed 24×7 triage.

Respond

Contain, eradicate and recover under agreed authority levels, with forensic evidence preserved throughout.

Improve

Quarterly review of coverage, drift and open risk. Detections and controls updated as the threat picture moves.

Model 01

Fully Managed

Cylentrix owns tooling, staffing and outcomes end to end. Suited to organisations without an in-house security team.

Model 02

Co-Managed

Your team keeps ownership and platform; we supply night, weekend and surge coverage plus detection engineering.

Model 03

Project Deployment

Fixed-scope design and implementation covering firewall migration, IAM rollout or Zero Trust build, with handover and documentation.

Model 04

Advisory & Retainer

Vendor-neutral architecture review, compliance advisory and a standby incident response retainer with guaranteed mobilisation.

07Technology Partners

Certified across the platforms
you already run.

Four cybersecurity vendors, each with certified engineers on staff. Recommendations stay vendor-neutral: if the right answer is to tune the licences you already hold rather than buy something new, that is what we will tell you.

  • Fortinet FortiGate NGFW, FortiAnalyzer and Security Fabric
  • Palo Alto Networks PAN-OS, Prisma Access and Cortex XDR
  • Sophos Intercept X endpoint protection and managed XDR
  • Check Point Software Quantum gateways, Harmony and threat prevention
Perimeter & Network

Fortinet FortiGate and Palo Alto PAN-OS: sizing, deployment, migration and day-two managed policy under change control.

Endpoint & XDR

Sophos Intercept X for behaviour-based protection, device isolation and managed XDR telemetry into our SOC.

Threat Prevention

Check Point Quantum gateways with IPS, sandboxing, URL filtering and SSL inspection tuned to your traffic profile.

Certified Delivery

Engineers hold current NSE, PCNSE, Sophos Architect and CCSA/CCSE credentials, revalidated on each vendor cycle.

08Clients

Enterprises that already
run on Cylentrix.

IT services, manufacturing, energy, pharmaceuticals, hospitality, infrastructure and education groups rely on us for managed security, managed IT and connectivity.
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
  • Cylentrix enterprise client
09Why Cylentrix

What changes when
one team is accountable.

Nine differences that show up in delivery, not in a capability matrix.

24×7 monitoring, staffed

A real analyst rota across follow-the-sun shifts, not an alert queue reviewed the next morning.

Certified engineers

Current vendor certifications across firewall, EDR, cloud and identity platforms, kept live through annual recertification.

Vendor-neutral consulting

We are not a single-vendor reseller. If tuning your existing licences solves the problem, we say so.

One accountable partner

Security, managed IT and connectivity under one contract, with no triage stalled by two suppliers pointing at each other.

Enterprise SLA

Written response and resolution targets by severity, reported monthly, with commercial consequences attached.

Rapid incident response

Retainer clients get same-day mobilisation, pre-agreed containment authority and preserved forensic evidence.

Compliance expertise

Practitioners who have been through ISO 27001, SOC 2, PCI-DSS and RBI/SEBI/IRDAI audits from the inside.

Pan-India deployment

Field engineering reach across metros and tier-2 cities for on-site rollout, replacement and audit support.

Global delivery

Operations spanning India, the USA and Singapore, supporting multi-region estates under consistent standards.

11Common Questions

Answers before
the first call.

The questions security and IT leaders ask us most often, answered directly. If yours is not here, a 30-minute call with an architect will cover it.

Ask a specific question
What cybersecurity services do you provide?

Fifteen services across five domains: detection and response (managed SOC, SIEM/SOAR, threat intelligence, incident response); network and perimeter (next-gen firewall, IDS/IPS, network security); identity (IAM, PAM, Zero Trust); workload and data (EDR/XDR, cloud security, DLP, application security and WAF, email security); and assurance (VAPT, red teaming, security audit and compliance).

Do you offer a managed SOC?

Yes. Our Security Operations Centre runs 24×7 with detection engineering mapped to MITRE ATT&CK, tiered analyst triage and defined response SLAs. It can be delivered fully managed or co-managed alongside your internal team, using either our SIEM platform or one you already own and want to keep.

Can you monitor cloud infrastructure?

Yes. We ingest control-plane and workload telemetry from AWS, Azure and Google Cloud, run continuous posture and entitlement checks against CIS benchmarks, and route confirmed findings into the same SOC queue as on-premises alerts, so cloud and datacentre risk are triaged together rather than in separate consoles.

Do you support Fortinet?

Yes. Fortinet is a core supported platform, alongside Palo Alto Networks, Cisco, Check Point, Sophos, Microsoft, VMware, Dell Technologies, HPE and Lenovo. We design, deploy, migrate and manage these estates, and because we are vendor-neutral, platform recommendations follow your requirements rather than a quota.

Can you secure remote and hybrid employees?

Yes. Remote access is secured through identity-anchored Zero Trust Network Access rather than flat VPN tunnels, combined with conditional access policies, device posture checks before authorisation, managed EDR on every endpoint, and DNS-layer filtering that applies whether the device is on or off the corporate network.

Do you help with ISO 27001 certification?

Yes, and beyond it. We support ISO 27001, SOC 2, PCI-DSS, HIPAA, GDPR, India's DPDPA, and the RBI, SEBI CSCRF and IRDAI frameworks. Engagements cover gap assessment, control design, evidence collection, internal audit support and direct liaison with your external auditor.

How quickly can deployment begin?

A security assessment typically starts within five working days of scoping. Managed SOC onboarding runs four to six weeks depending on log source count and environment complexity. Firewall and endpoint deployments are phased around your change windows. Emergency incident response is mobilised the same day under an active retainer.

Do you provide 24×7 support?

Yes. SOC monitoring and incident response operate 24×7×365 across follow-the-sun shifts. Every managed engagement carries a written SLA with severity-based response targets and a named client success lead who is accountable for meeting them.

REQUEST A SECURITY ASSESSMENT

Start with what
you already own.

The assessment is a working session, not a sales call. A Cylentrix architect reviews your current controls, identifies the gaps that matter most, and gives you a prioritised view of risk, whether or not you engage us afterwards.

  • Architect-led, not SDR-ledYour first conversation is with an engineer who has built these environments.
  • Prioritised gap reportFindings ranked by exploitability and business impact, with an effort estimate for each fix.
  • Vendor-neutral recommendationsOptions include tuning what you have. No licence is proposed before the gap is proven.
  • Clear commercialsScope, timeline, SLA and pricing in writing before any work begins.
▸ RESPONSE WITHIN 1 BUSINESS DAY
▸ NDA SIGNED BEFORE ANY TECHNICAL DETAIL IS SHARED
▸ ACTIVE BREACH? CALL +91 99222 30055

Request an Security assessment

Tell us what you are trying to find. We will match you with the right solution.