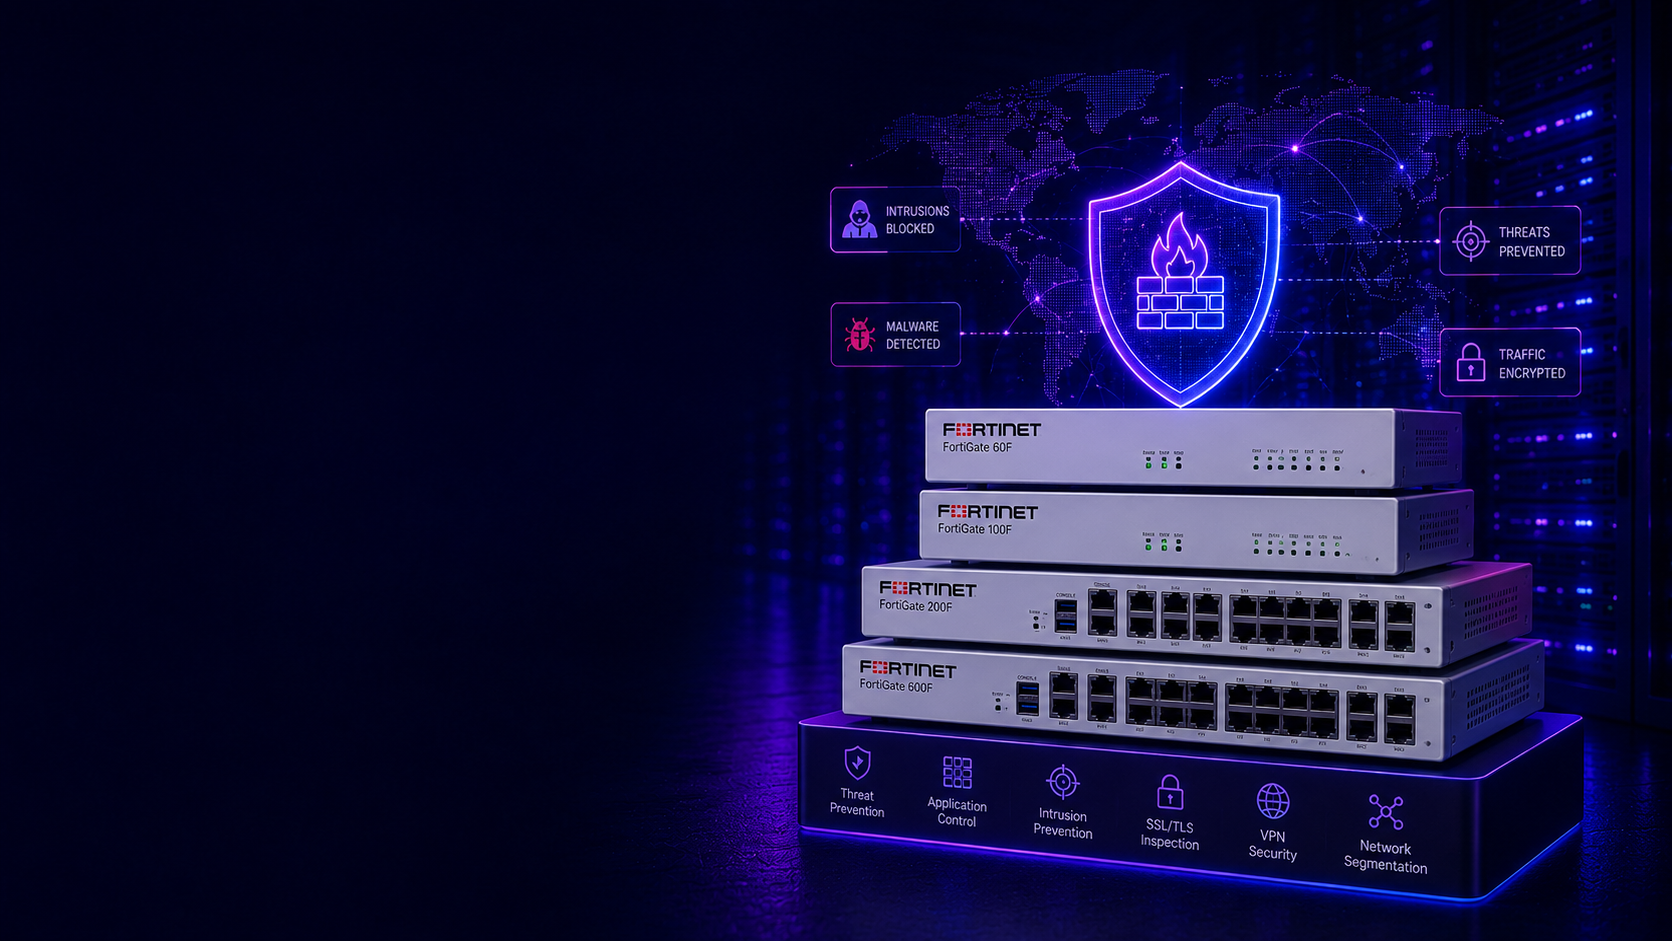
Secure enterprise networks with intelligently configured next-generation firewalls that combine traffic control, application visibility, threat prevention and continuous security management. Cylentrix designs, deploys and operates enterprise NGFW platforms as a managed firewall service, so network security keeps pace with the business it protects.
A next-generation firewall (NGFW) understands what is moving through the network, who is moving it and whether it is safe. Cylentrix designs, deploys and manages enterprise NGFW platforms end-to-end.
Traditional firewalls control traffic by IP address, port and protocol. A modern next-generation firewall adds application awareness, user identity and deep traffic inspection, combining intrusion prevention, malware protection, web security and VPN behind one centralized policy.
Our managed firewall service covers the full lifecycle: architecture and policy design, deployment, 24×7 monitoring, rule optimization, firmware updates and formal change management, so the firewall keeps enforcing what the business intends.
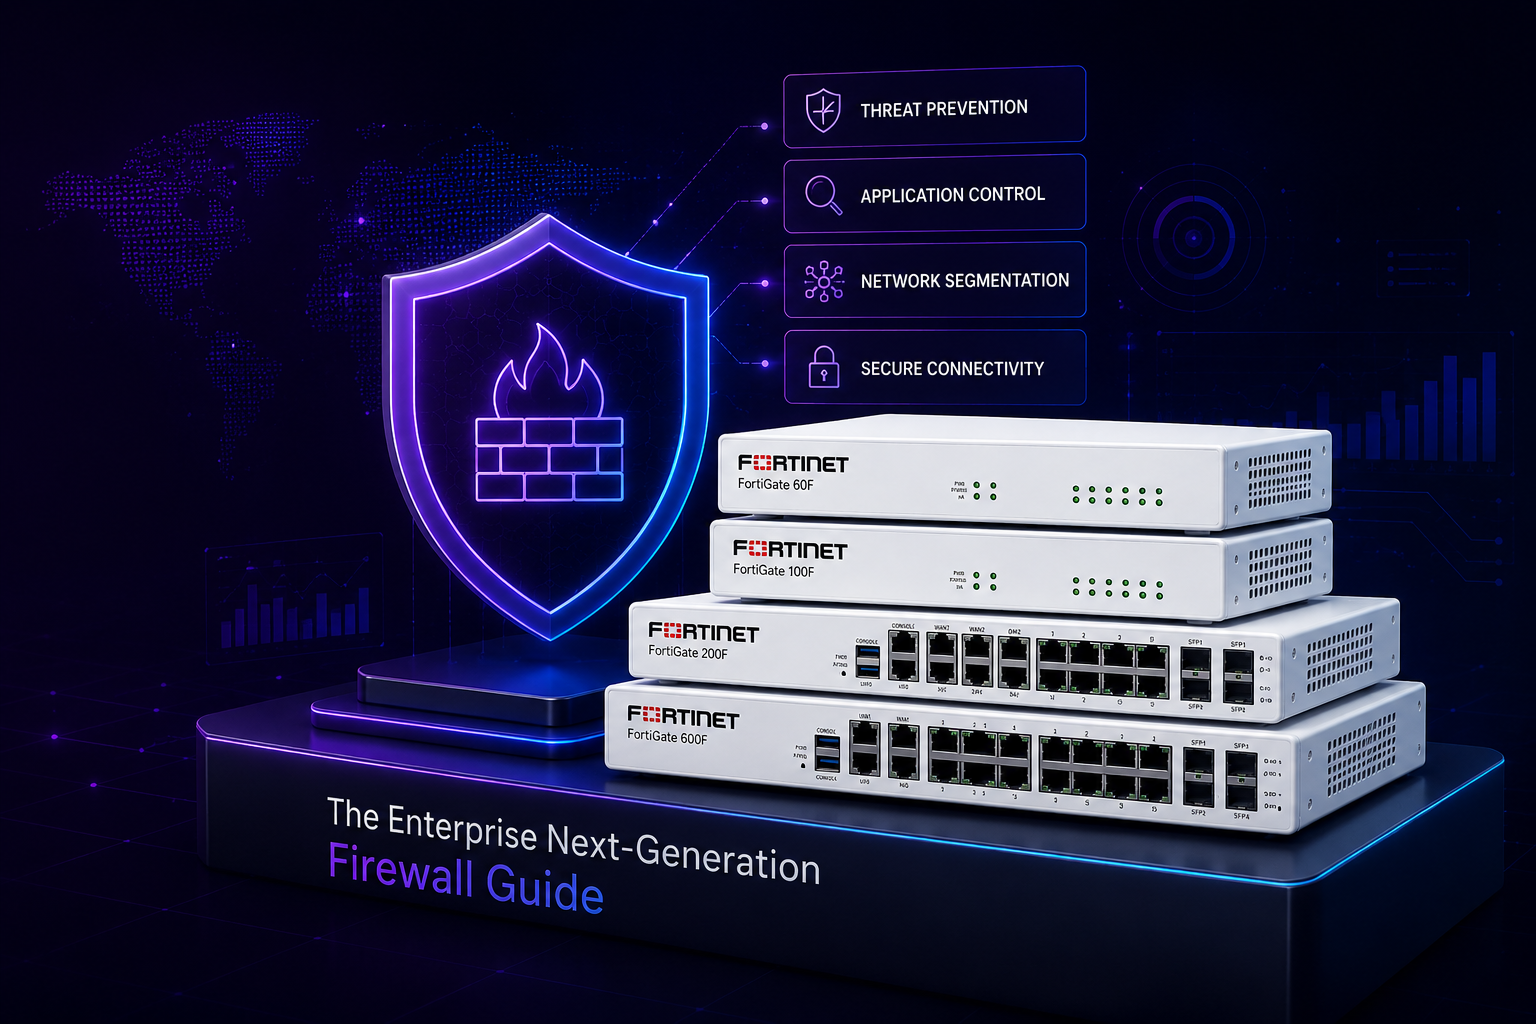
Identify and govern traffic by application and user, not just port and protocol.
IPS, anti-malware and threat intelligence that block attacks inside allowed traffic.
Inspect encrypted traffic where policy permits and control risky web destinations.
Secure zones, encrypted remote access and continuous firewall management.
Firewall deployment is an engineering exercise, not an unboxing. Every Cylentrix NGFW engagement follows a controlled lifecycle from assessment through go-live to ongoing managed operations.
Understand current infrastructure, traffic patterns, applications and security requirements.
Develop firewall architecture, security zones, policies and the connectivity approach.
Configure security policies, NAT, VPN, application controls and security profiles.
Implement the firewall with controlled change management and minimal disruption.
Test connectivity, security controls and policy behaviour before sign-off.
Monitor 24×7, review rules, apply firmware updates and manage every change.
Managed operations: 24×7 monitoring · rule optimization · config backup · firmware updates · change management
Cloud platforms, branch offices, remote users and SaaS now share one network. A well-designed, well-managed NGFW turns that complexity into visibility, control and lower risk.
Layered IPS, anti-malware and threat prevention help block attacks hiding inside allowed traffic.
See applications, users and destinations across sites, cloud and remote workers in one view.
Encrypted VPN and consistent policy for branches, SaaS and IaaS, wherever users connect from.
Segmentation, logging and policy evidence that support ISO 27001, PCI DSS and GDPR requirements.
Cylentrix runs monitoring, rule hygiene, firmware and change management, so your team doesn’t have to.
Analytics surface anomalous flows and rank events, so analysts focus on what matters first.
Every regulated or distributed enterprise routes its critical traffic through its firewalls. Cylentrix designs NGFW controls for the industries where that traffic can never be left to a port-based guess.
Segments OT and plant networks from IT, keeping compromised endpoints off the line.
Protects EHR, PACS and connected medical devices with strict zoning and inspected clinical traffic.
Application-aware controls and audited security policies around core banking, trading and payment systems.
Governs client VPNs, developer tooling and SaaS traffic across delivery centres.
Web filtering and application control for campus networks serving thousands of users on shared infrastructure.
Isolates POS and payment traffic from guest Wi-Fi and back-office systems.
Secures hub, warehouse and tracking systems across a distributed site footprint.
Zoned, policy-driven perimeters for citizen services and department connectivity.
High-throughput inspection and segmentation for north-south and east-west traffic.
Separates guest Wi-Fi from PMS, payment and operations networks at every property.
Anyone can rack a firewall. Cylentrix brings cybersecurity, managed IT and telecom expertise to one table, so the firewall is designed into your network architecture and operated as part of your security posture.
Cybersecurity, IT and telecom under one practice, so the firewall is designed as part of the wider security architecture, not a box on a rack.
Deep enterprise network knowledge: routing, zones, WAN and cloud paths shape every firewall design we deliver.
One accountable owner for firewall design decisions, policy changes and escalations across every site.
An assess-to-optimize lifecycle with controlled change management, so cutovers happen with minimal disruption.
Firewall health, policy activity and threat events watched around the clock, with AI-assisted analytics prioritizing what matters.
Enterprise NGFW deployment and managed firewall operations delivered across all three regions under one standard.
Security engineers experienced across leading enterprise NGFW platforms design, configure and support every deployment.
Recurring rule review and optimization keep policy bases lean, auditable and aligned with business change.
NGFW controls integrate with SOC monitoring, endpoint security and zero-trust initiatives where required.
Cylentrix designs, deploys and manages enterprise firewall estates built on the industry’s leading next-generation firewall platforms.
Practical guides from the Cylentrix security practice, written for the teams who will own the firewall, not the people selling it.
Buyer's Guide
What an NGFW is, which capabilities matter, and how to evaluate platforms for an enterprise network.
Read the guide
Best Practices
Zoning, policy design, change control and rule hygiene for firewalls that stay clean over time.
Read the playbook
Strategy
How inspection, segmentation and threat prevention combine into a defensible network architecture.
Read the guideThe questions security and network leaders ask before an NGFW project, answered the way our firewall engineers answer them.
A Next-Generation Firewall is a network security platform that goes beyond traditional port- and IP-based filtering. Alongside stateful traffic control, an NGFW can identify applications and users, inspect traffic for intrusions and malware, filter web destinations and enforce centralized security policies, making it the primary control point for enterprise network traffic.
A traditional firewall decides based on IP addresses, ports and protocols. An NGFW adds application awareness, user identity context, intrusion prevention, threat prevention and, where permitted, SSL/TLS inspection. That means it can distinguish a sanctioned business application from a risky one on the same port, and block threats hidden inside allowed traffic.
Core NGFW capabilities include application control, intrusion prevention (IPS), threat and malware prevention, URL and web security, SSL/TLS inspection, user-based security policies, VPN and secure remote access, and network segmentation. Cylentrix configures these capabilities to match each organisation's security policy and traffic profile.
Yes. NGFW platforms can identify traffic at the application level and, where identity sources are integrated, apply policies per user or group. This allows rules such as permitting a collaboration suite for all staff while restricting file-sharing applications to approved teams, instead of blunt port-based allow or deny.
Most modern NGFW platforms support SSL/TLS inspection, decrypting selected traffic for security analysis before re-encrypting it. Because encrypted inspection has privacy, compliance and performance implications, Cylentrix scopes it carefully: which traffic categories are inspected, which are exempt, and how the design aligns with organisational policy.
Yes. Firewalls can be deployed at data centres, branch perimeters and cloud edges, with site-to-site VPNs, remote-access VPNs and segmentation extending consistent security policy across the environment. Cylentrix designs the firewall architecture around how your sites, clouds and users actually connect.
Firewall policies drift: rules accumulate, applications change and threats evolve. Without regular rule review, monitoring and optimization, a well-deployed firewall gradually becomes permissive and slow. Managed firewall operations keep policies aligned with business requirements, configurations backed up, software current and security events watched continuously.
Cylentrix delivers the full lifecycle: assessment, firewall architecture and policy design, configuration, controlled deployment, validation and ongoing managed firewall operations, including monitoring, policy management, rule optimization and configuration backup, delivered by a team that spans cybersecurity, managed IT and telecom across India, USA and Singapore.
Strengthen network visibility, control application traffic and protect critical infrastructure with a next-generation firewall strategy designed around your enterprise environment. Also explore our cybersecurity services, Managed SOC and Zero Trust Architecture.
Tell us about your network and what you need the firewall to do. A Cylentrix security engineer will review your requirements and come back with a practical NGFW recommendation, scope and quote.
Share a few details and we will get back to you with next steps.