Cylentrix

SOC OPERATIONAL • 24/7 India • USA • Singapore
CYBERSECURITY · SIEM & SOAR

SIEM & SOAR Services for
Smarter Security Operations

Bring security events, threat intelligence and security alerts into one intelligent security operations layer with SIEM-powered visibility and SOAR-driven response automation. Cylentrix designs, implements and manages Security Information and Event Management alongside Security Orchestration, Automation and Response, so security analytics, event correlation and incident response run as one connected workflow instead of a dozen disconnected consoles.

  • SIEM ImplementationDesign · Deploy · Tune
  • SOAR AutomationPlaybook-Driven Response
  • Security AnalyticsCorrelation & Detection
  • 24×7 MonitoringManaged SIEM Services
  • India · USA · SingaporeGlobal Delivery
01OVERVIEW

Turn Security Data
Into Action

Two technologies, one operating model. SIEM tells you what is happening across the environment; SOAR decides and executes what happens next.

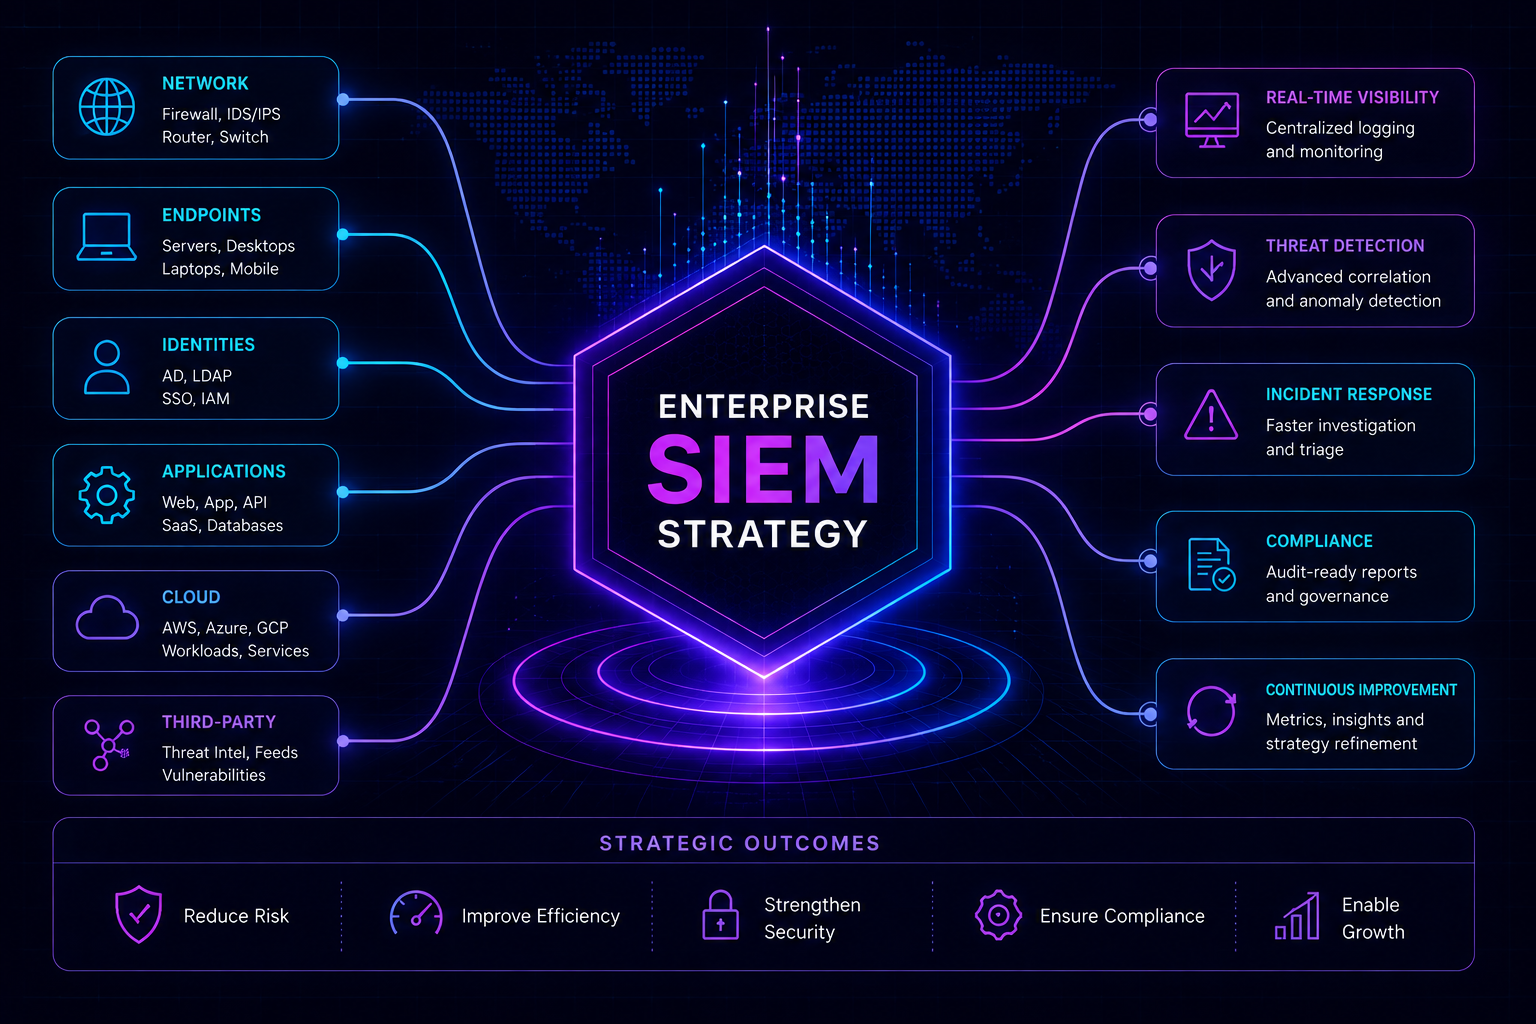
SIEM, or Security Information and Event Management, provides centralised visibility. It collects logs and security events from across the estate, normalises them into a common format, correlates related activity and applies security analytics to surface what actually warrants attention.

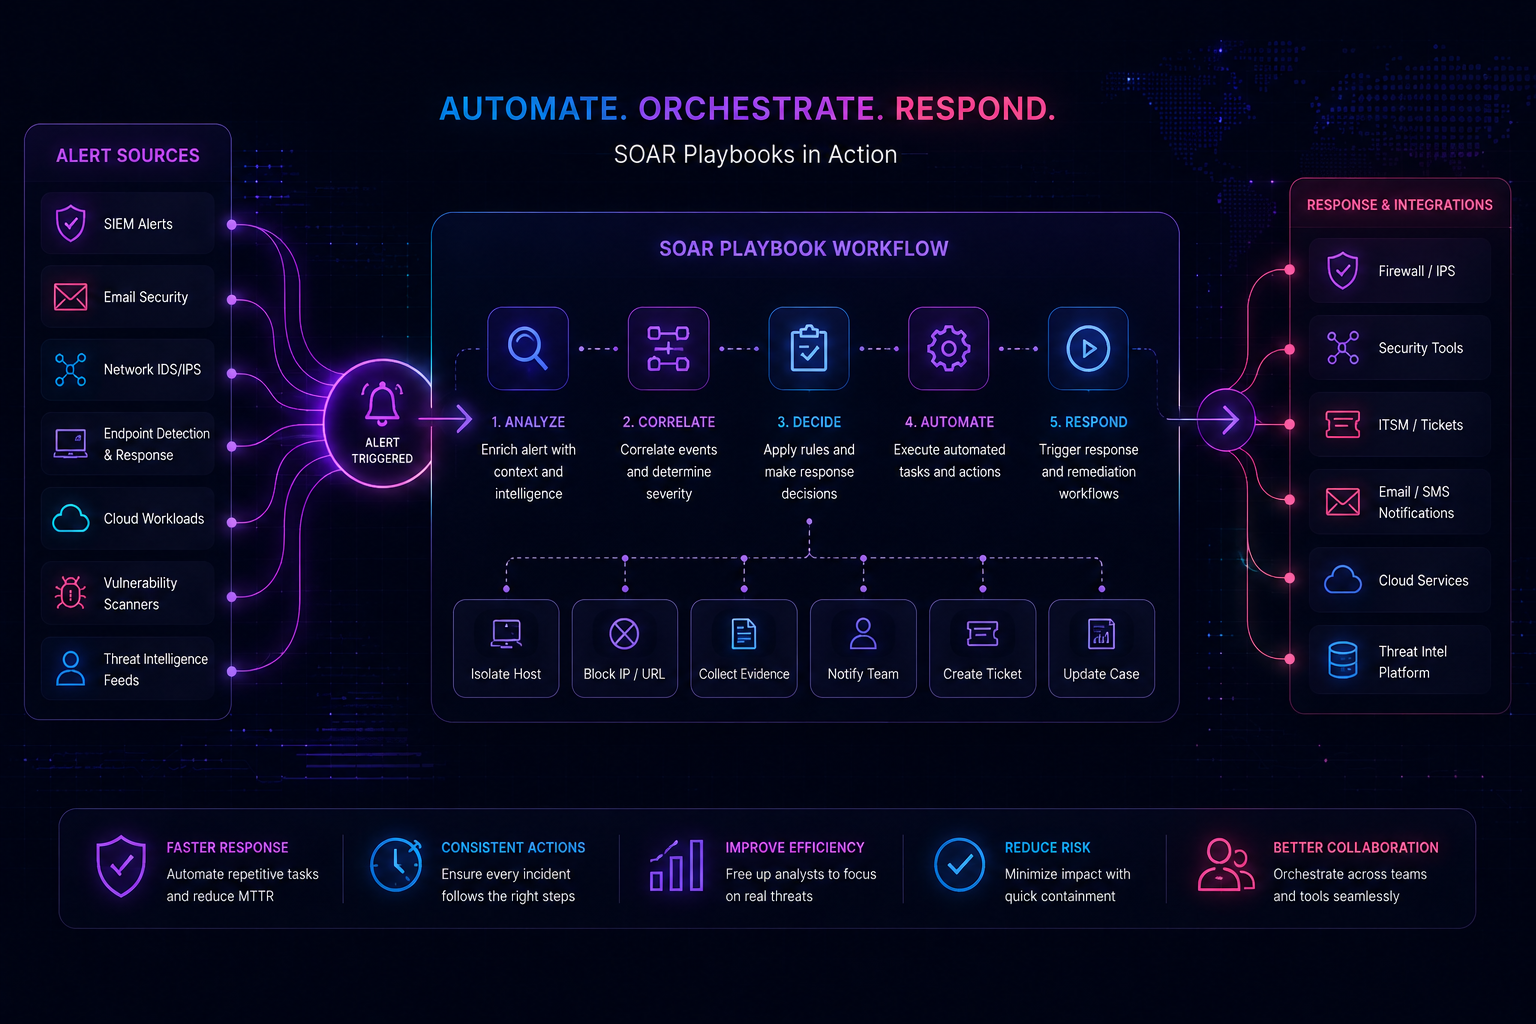
SOAR, or Security Orchestration, Automation and Response, provides consistency and speed. It connects the tools already in use and runs playbooks that enrich alerts, carry out repetitive investigation steps and execute approved response actions.

Used together, they move a security team along a single continuous path rather than a queue of disconnected alerts.

  • Centralized Visibility

    Every relevant source in one security data layer.

  • Intelligent Correlation

    Related events joined into one meaningful signal.

  • Automated Workflows

    Repetitive investigation steps run the same way every time.

  • Faster Response

    Less manual handling between detection and containment.
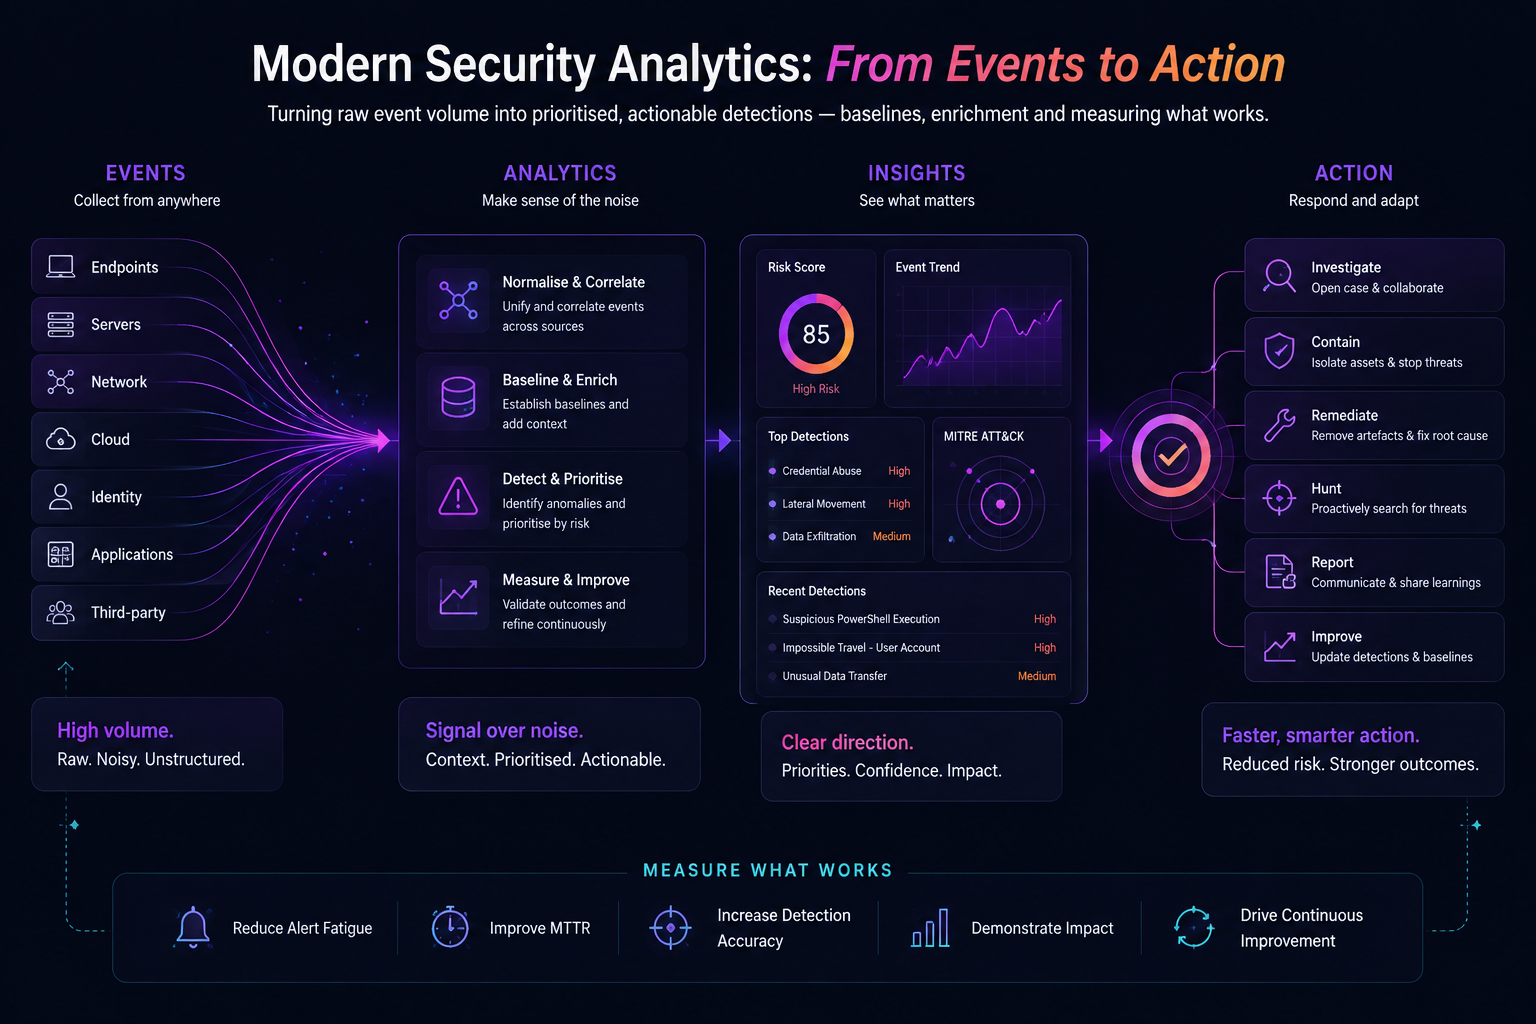
Alerts, analysis, decision, response: security events arrive from every monitored source, correlation and security analytics separate signal from noise, enrichment and triage establish severity, scope and owner, and SOAR playbooks execute containment and remediation steps
02HOW IT WORKS

From Security Events to
Automated Response

One pipeline: data sources feed the SIEM, the SIEM feeds SOAR, and SOAR closes the loop back into the tools that carry out the action.

Data Sources

Ingest
  • Endpoints
  • Network
  • Firewall
  • Cloud
  • Identity
  • Applications
  • Email

SIEM Layer

Detect
  • Collect

    Logs and security events ingested from every onboarded source.

  • Normalize

    Different formats mapped to one common schema.

  • Correlate

    Related activity joined across sources into a single narrative.

  • Analyze

    Behaviour compared against baselines and detection content.

  • Detect

    Prioritised detections raised with supporting evidence.

SOAR Layer

Respond
  • Enrich

    Threat intelligence, asset and user context attached automatically.

  • Investigate

    Routine lookups and evidence collection run across the stack.

  • Automate

    Playbooks apply triage, ticketing and routing consistently.

  • Respond

    Approved containment and remediation executed through existing tools.

Data Sources Collect Correlate Detect Enrich Investigate Automate Respond
03BUSINESS BENEFITS

What enterprises gain
from SIEM & SOAR

The measurable outcomes of running security analytics and response automation as one managed capability rather than a collection of tools.

  • Complete Security Visibility

    Endpoint, network, firewall, cloud, identity, application and email events in one security data layer, so nothing sits unmonitored in a silo.

  • Less Alert Noise

    Event correlation and tuned detection content cut false positives, so the queue reflects real risk instead of raw volume.

  • Faster Incident Response

    SOAR playbooks handle enrichment, triage and approved containment, reducing the manual handoffs between detection and action.

  • Consistent, Repeatable Process

    The same incident is handled the same way on any shift, because response steps are documented, version-controlled and automated.

  • More Analyst Capacity

    Automating repetitive lookups and ticketing frees skilled people to investigate the threats that actually need human judgement.

  • Audit-Ready Reporting

    Retained, searchable security event history supports internal review, security reporting and evidence requests without a manual scramble.

  • Value From Existing Tools

    Firewalls, EDR, identity, cloud and email security are integrated as data sources and response endpoints rather than replaced.

  • Scales Without Rebuilding

    New log sources, sites and cloud workloads are onboarded into the same SIEM and SOAR pipeline as the estate grows.

05WHY CYLENTRIX

Why enterprises choose Cylentrix
for SIEM & SOAR

A SIEM is only as good as the environment it understands. Cylentrix builds security operations on top of infrastructure knowledge, not in isolation from it.

Cybersecurity, IT and telecom under one roof

The same organisation that secures the estate also runs the networks and systems generating the events, so context is not lost between vendors.

SIEM implementation and management

Use-case design, log source onboarding, deployment, tuning and ongoing rule maintenance, delivered as a managed capability.

SOAR automation designed around your process

Playbooks are written to match how your team already escalates and approves, then automated, not imposed as a generic template.

Security analytics expertise

Correlation rules, behavioural baselines and detection content developed and reviewed by engineers who work in the consoles daily.

Threat intelligence integration

Relevant intelligence feeds are wired into detection and enrichment so indicators are recognised at the moment they appear.

Integration with your existing stack

Firewalls, EDR, identity, cloud, email security and ITSM are connected through native integrations and APIs rather than replaced.

24×7 security operations

Continuous monitoring and response coverage, with escalation paths agreed before an incident rather than during one.

Enterprise infrastructure visibility

Network, endpoint, cloud and identity telemetry mapped to one architecture, so coverage gaps are identified before they matter.

India, USA and Singapore presence

Multi-region delivery and support for enterprises operating across time zones and differing data-handling expectations.

06PARTNERS

Technology &
Security Partners

Cylentrix implements SIEM and SOAR on enterprise-grade platforms and integrates them with the security tooling already deployed in your environment.

  • FortiSIEM Security information and event management with correlation, analytics and reporting
  • Seceon Security analytics platform for threat detection and automated response
08FAQ

SIEM & SOAR,
answered directly

The questions security and IT leaders ask before committing to a SIEM and SOAR programme.

What is SIEM?

SIEM stands for Security Information and Event Management. A SIEM platform collects logs and security events from across the environment: endpoints, networks, firewalls, cloud platforms, identity systems, applications and email. It then normalises, correlates and analyses that data to surface suspicious activity. It gives security teams centralised visibility, security analytics, threat detection and the historical record needed for investigation, reporting and audit.

What is SOAR?

SOAR stands for Security Orchestration, Automation and Response. A SOAR platform connects the security tools already in use and runs defined workflows, called playbooks, across them. It can enrich an alert with threat intelligence and asset context, carry out repetitive investigation steps, triage and assign incidents, and execute approved containment actions, so analysts spend their time on judgement rather than repetition.

What is the difference between SIEM and SOAR?

SIEM is about visibility and detection: it aggregates and correlates security data to identify what is happening. SOAR is about orchestration and action: it takes what has been detected and runs a consistent, largely automated response across the security stack. In short, SIEM answers what happened and why it matters, while SOAR answers what should happen next and executes it. Most enterprises deploy them together, with the SIEM feeding prioritised detections into SOAR playbooks.

Why do enterprises need SIEM and SOAR?

Enterprise environments generate far more security events than any team can review manually, spread across dozens of tools that do not share context. SIEM consolidates that data and correlates it so meaningful threats stand out from routine noise and false positives. SOAR then standardises the response so investigation and containment do not depend on which analyst is on shift. Together they improve visibility, consistency and analyst capacity, and support compliance reporting.

What data sources can SIEM collect?

A SIEM can ingest data from endpoints and EDR agents, servers and operating systems, firewalls, network devices, proxies and VPN gateways, identity and access management systems such as Active Directory and SSO providers, cloud platforms including AWS, Azure and Google Cloud, SaaS and business applications, databases, email security gateways and other security tools. Cylentrix scopes source onboarding to the data that actually supports your detection and reporting use cases.

Can SIEM and SOAR integrate with existing security tools?

Yes. Both are designed to sit on top of an existing security estate rather than replace it. Integration is typically through native connectors, APIs, syslog forwarding and agents, covering firewalls, EDR and XDR, identity providers, cloud platforms, email security, vulnerability management, threat intelligence feeds and ITSM or ticketing systems. Cylentrix assesses the current stack first and designs the integration around what is already deployed.

How does SOAR automate security incident response?

SOAR uses playbooks: predefined workflows triggered by an alert or detection. A playbook can enrich the alert with threat intelligence, reputation data and asset ownership, gather related evidence from other tools, apply triage logic to set severity, open and route a ticket, and then execute containment actions such as isolating a host, disabling an account or blocking an indicator. Higher-impact actions are normally placed behind analyst approval, so automation accelerates the work without removing human oversight.

How can Cylentrix help with SIEM and SOAR?

Cylentrix designs, implements and manages SIEM and SOAR as one security operations layer, covering use-case and log-source design, SIEM deployment and tuning, correlation rule and analytics development, threat intelligence integration, SOAR playbook design and automation, and integration with existing security, IT and network infrastructure. Because Cylentrix also delivers managed IT and telecom services, the same team understands the infrastructure the security data comes from. Delivery is supported across India, USA and Singapore.

GET STARTED

Turn Security Events Into
Faster, Smarter Response

Strengthen security visibility, automate repetitive response workflows and help your security team focus on the threats that matter most. Explore related services: Managed SOC, Zero Trust Architecture and enterprise cybersecurity.

09TALK TO US

Talk to a
Security Expert

Tell us what you are running today and what you need to see. We will come back with a scoped view of the SIEM and SOAR build that fits your environment.

  • A security engineer replies, not a call-centre form handler.
  • We review your existing log sources and security tooling first.
  • Scoping covers SIEM use cases, log volume and SOAR playbook design.
  • Delivery and support across India, USA and Singapore.

Request a SIEM & SOAR consultation

Share a few details and the security operations team will get back to you.

Prefer email? Write to sales@cylentrix.com or use the contact page.