Turn global and external threat signals into actionable intelligence that helps security teams understand emerging threats, identify relevant risks and strengthen proactive defence. Cylentrix combines cyber threat intelligence collection, structured threat intelligence analysis and risk-based prioritisation, so the intelligence reaching your analysts is the intelligence that actually matters to your environment.
Threat actors, campaigns, vulnerabilities, malicious infrastructure and attack techniques change constantly, and most of that change happens outside your perimeter, where your controls cannot see it.
Threat Intelligence is the practice of collecting, analysing and contextualising information about threats so an organisation can make better-informed security decisions. It is not another alert stream. It is the context that explains which alerts, vulnerabilities and external signals deserve attention first, and why.
Without that context, every security signal looks equally urgent. Threat intelligence helps security teams understand what is relevant to their sector, technologies and exposure, so effort goes where the risk actually is rather than being spread evenly across everything.
Identify relevant developments across the evolving threat landscape before they reach your environment.
Understand activity associated with relevant threat groups, campaigns and observed behaviour.
Monitor indicators such as suspicious domains, IP addresses and hosting infrastructure.
Track vulnerability intelligence that may affect business-critical technologies you actually run.
Identify external threats targeting organisational identities, domains and digital presence.
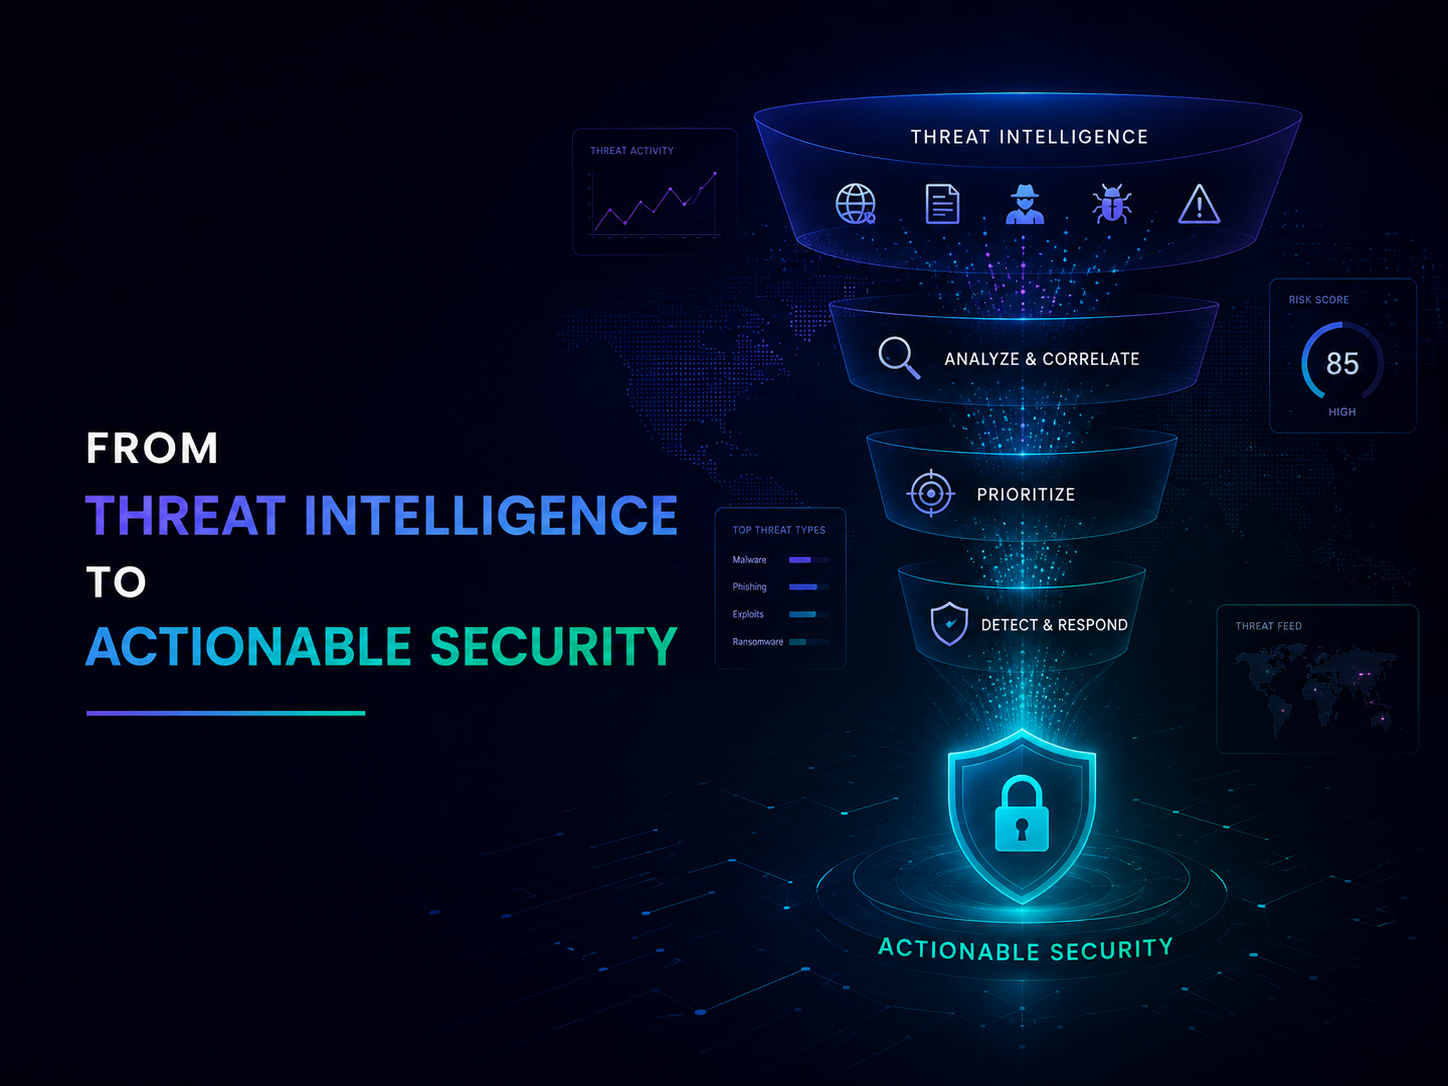
Threat intelligence is only valuable when it becomes actionable. This is the path a signal travels, from the sources it arrives on to the moment it changes what a security team does next.
Relevant external threat data and indicators.
Information about vulnerabilities and associated risk.
Relevant publicly available threat information.
Monitoring for relevant exposed information and threat activity.
Telemetry that adds context when combined with external intelligence.
Gather relevant threat signals against defined requirements.
Assess source reliability and indicator quality before use.
Add context from vulnerabilities, assets and known activity.
Connect intelligence with relevant internal security information.
Determine what matters most to this organisation, in this context.
Provide intelligence that supports concrete security decisions.
AI-assisted correlation supports analysts, it does not replace them
The value of threat intelligence shows up in decisions: what gets fixed first, how quickly an investigation closes, and how much of your exposure you knew about in advance.
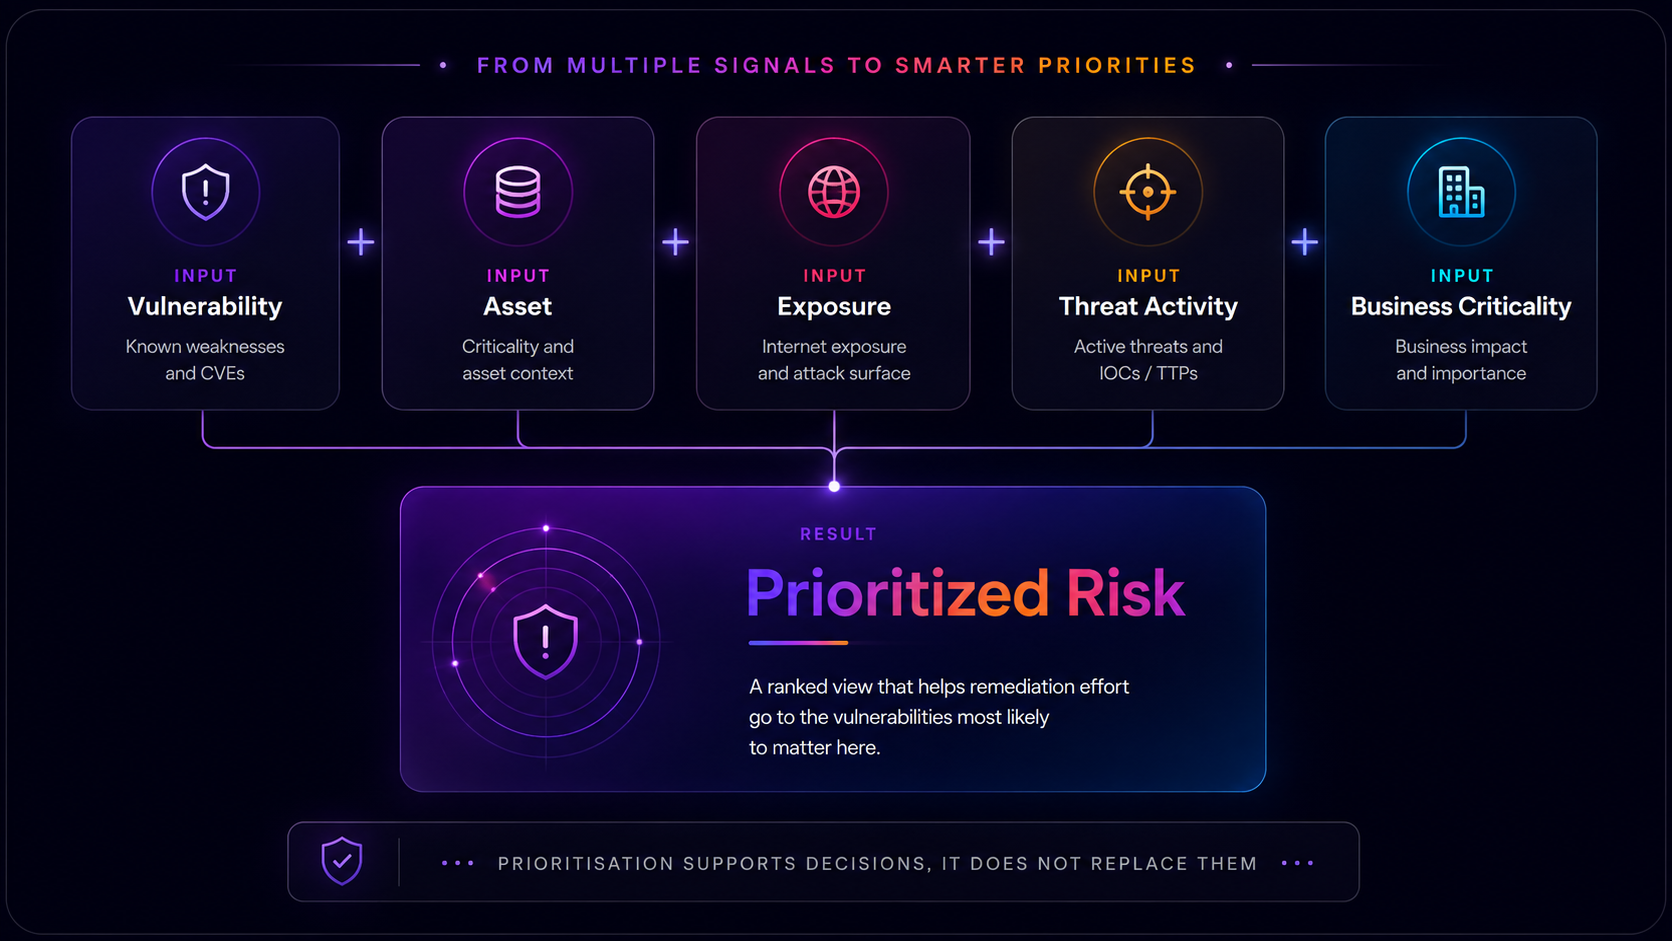
Vulnerability intelligence weighed against asset, exposure and threat activity helps teams fix what reduces the most risk first.
Emerging threats, threat actor activity and campaign intelligence surface while there is still time to prepare.
SIEM and SOC alerts arrive enriched with IOC and IOA context, so analysts spend less time reconstructing background.
Brand, domain and dark web monitoring helps identify exposure sitting outside the perimeter, where controls cannot see it.
Threat intelligence reports written for analysts and leadership support security planning and investment decisions.
Threat exposure is not evenly distributed. Attacker interest follows data, money, uptime and dependency, which is why intelligence has to be read against the sector it applies to.
Financial fraud, credential leaks and brand impersonation make external threat monitoring a supervisory expectation.
Patient data and clinical uptime draw sustained attention, so vulnerability intelligence shapes patching order.
Downtime carries an hourly cost, so intelligence on OT and supplier threats shapes continuity planning.
Serving many clients from one platform raises the stakes for supply-chain and credential intelligence.
Citizen services and public portals face targeted interest, making threat actor intelligence routine assurance.
Payment flows and consumer trust make look-alike domains and fake storefronts a constant monitoring concern.
Open campuses and shared devices create wide exposure, where credential and phishing intelligence pays back fast.
Interconnected operators mean a partner's exposure becomes yours, so third-party intelligence matters.
Intelligence is only as useful as the operational understanding behind it. Cylentrix reads threat data through the lens of the environments we secure, run and connect every day.
We secure, operate and connect enterprise environments, so intelligence is assessed against how your infrastructure is actually built.
Feeds are a starting point, not a deliverable. Our analysts assess reliability, relevance and confidence before anything is escalated.
Because we run security operations, we know which intelligence a SOC can act on and which simply adds volume.
External signals, brand and domain activity and emerging threats are tracked continuously rather than reviewed periodically.
Intelligence is ranked against your assets, exposure and business criticality, so effort lands where the risk concentrates.
Our architecture practice means findings arrive with a view of which controls already mitigate them and which do not.
When something does happen, the intelligence gathered beforehand becomes context for responders instead of a separate exercise.
Reporting is written for the people who act on it: analysts, security leadership and the executives who fund the response.
Teams across three regions give both local threat context and a view of activity that crosses borders.
Cylentrix works with established security technology providers so intelligence integrates with the platforms already in place, rather than adding another disconnected console.
Practical guides from the Cylentrix security practice, written for the teams who will use threat intelligence day to day.
Enterprise Guide
What a threat intelligence capability is made of, what it should produce, and how to tell whether it is working.
Read the guide
Threat Landscape
How to read threat actor reporting critically, and how to decide which campaigns are relevant to your sector.
Read the guide
Operations
Turning validated intelligence into detections, hunts and remediation priorities inside existing workflows.
Read the paperThe questions security leaders ask before building or buying a threat intelligence capability, answered the way our analysts answer them.
Threat Intelligence is the collection, analysis and contextualisation of information about threats so an organisation can make better-informed security decisions. It goes beyond raw data by assessing where a signal came from, how reliable it is, and whether it is relevant to a specific environment. The output is intelligence a security team can act on, rather than more data to triage.
Cyber Threat Intelligence (CTI) is threat intelligence applied to cyber risk specifically: threat actors, campaigns, malware behaviour, malicious infrastructure, vulnerabilities and external exposure. It is usually described at three levels: strategic intelligence for leadership decisions, operational intelligence about campaigns and actor behaviour, and tactical intelligence covering indicators and techniques used in detection.
It helps security teams decide where to focus. Threat intelligence supports earlier awareness of emerging threats, gives investigations external context, informs which vulnerabilities to remediate first, and highlights external exposure such as impersonated domains or leaked credentials. It supports proactive defence and better prioritisation, but it does not guarantee that every threat will be detected or prevented.
Indicators of Compromise (IOCs) are observable artefacts associated with malicious activity, such as malicious IP addresses, domains, URLs, file hashes and suspicious infrastructure. They are useful for detection and retrospective searching, but they age quickly as attackers rotate infrastructure, and an IOC on its own does not tell you whether your organisation was affected.
Indicators of Attack (IOAs) describe suspicious behaviours, attack patterns, anomalous activity and known tactics and techniques, rather than the artefacts an attacker leaves behind. Because behaviour changes more slowly than infrastructure, IOAs often remain relevant longer than IOCs and can support detection earlier in an attack sequence.
Severity scores alone do not indicate urgency for a specific organisation. Vulnerability intelligence adds context on whether a vulnerability affects technologies actually in use, whether it is associated with observed threat activity, whether affected systems are externally exposed, and how business-critical those systems are. Combining those factors produces a prioritised view that helps remediation effort go where it reduces the most risk.
Yes. Threat intelligence is commonly used to enrich SIEM correlation with external context, to give SOC analysts a broader view when investigating suspicious activity, to support hypothesis-driven threat hunting, and to provide context during incident response. Integration is where intelligence becomes operational, which is why it should be planned around existing detection and response workflows rather than delivered as standalone reporting.
Cylentrix helps define intelligence requirements, select and evaluate relevant sources, and establish analysis and prioritisation processes suited to the organisation's sector and technology footprint. Because we also deliver security operations, architecture and incident response, intelligence is assessed against how your environment is actually built and integrated into the workflows that already exist. Teams across India, USA and Singapore provide both local threat context and a view of cross-border activity.
Gain clearer visibility into emerging threats, external exposure and relevant threat activity with intelligence designed to support proactive security decisions. Tell us what you are trying to protect and a Cylentrix security specialist will get back to you.